AEGIS: the SOC that fights back
Most security tools detect and then wait for a human. AEGIS closes the loop: it detects an attack, investigates it and blocks it, with no human in between.
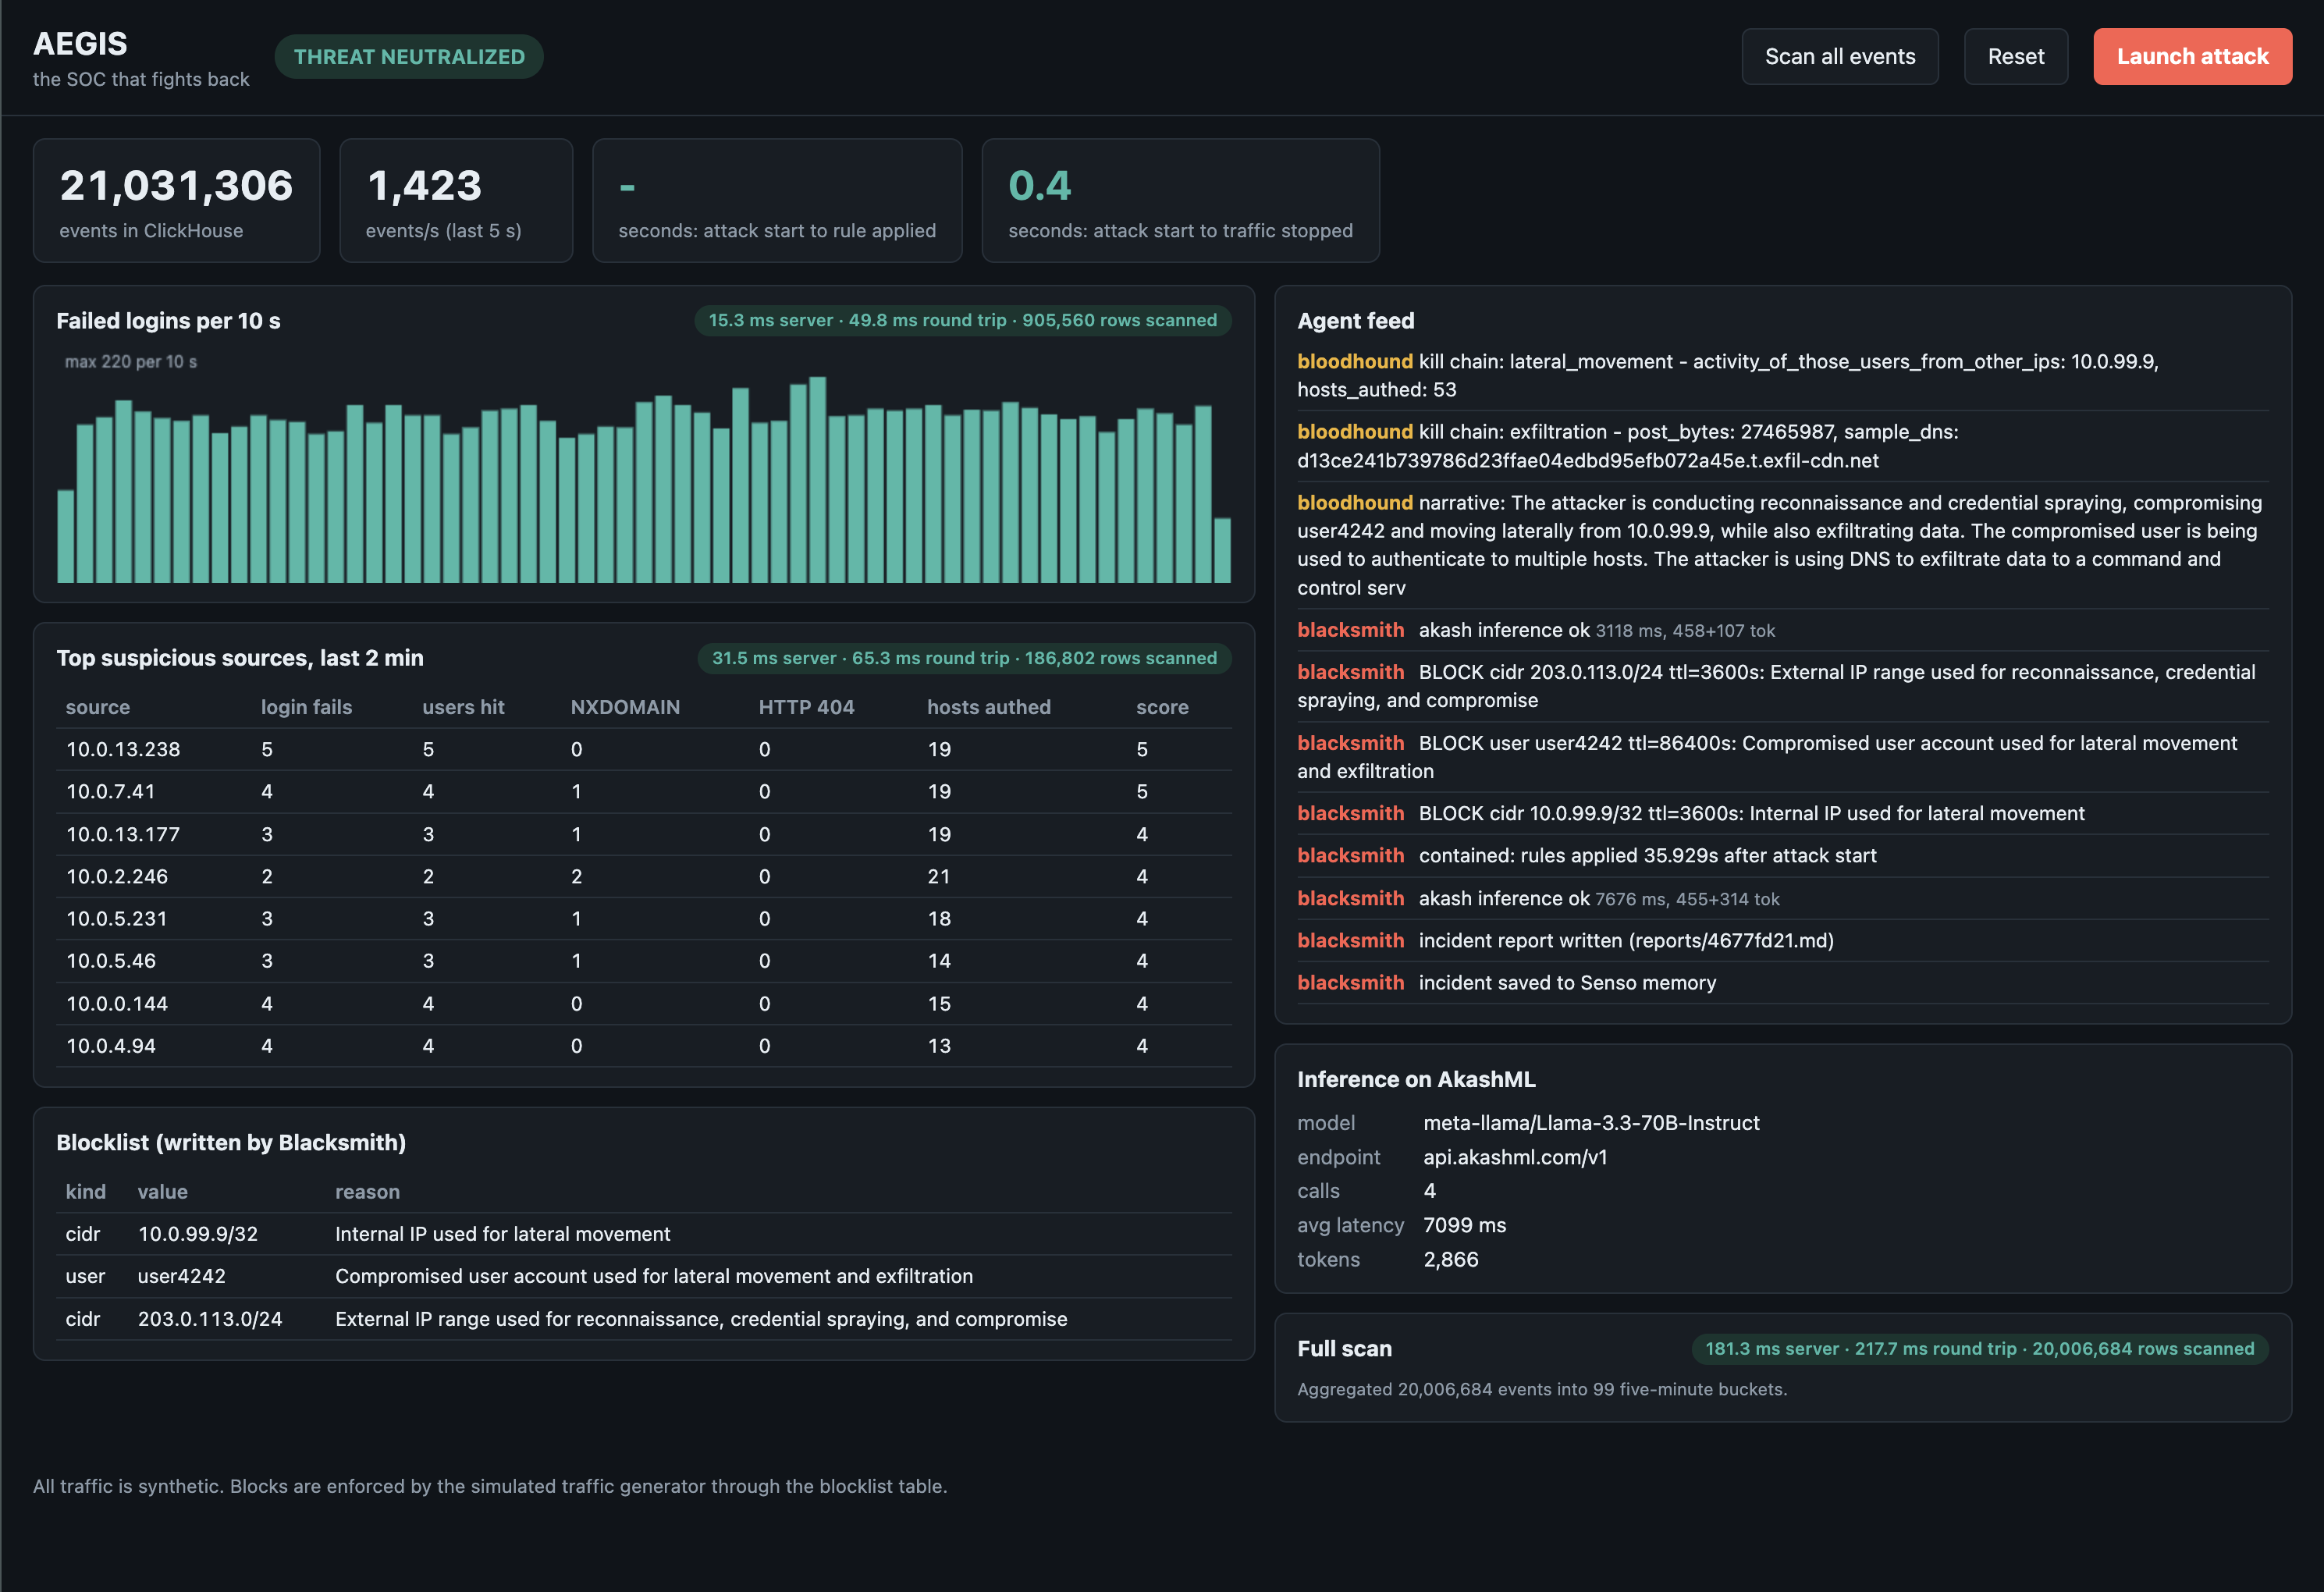
Synthetic attack traffic (recon, password spray, an account compromise, lateral movement through an internal host, and DNS-tunnel exfiltration) streams into ClickHouse Cloud, which holds about 11M events. Three agents then run:
Sentinel runs a ClickHouse query over recent events to cut millions of rows to a few suspect sources, and an open model on AkashML judges them.
Bloodhound pulls the suspect’s timeline with SQL, maps it to kill-chain stages and narrates it. It also searches Senso for similar past incidents.
Blacksmith proposes block rules, and our code validates them (external ranges no wider than /24, internal hosts only as exact /32, users only if confirmed compromised) and adds any confirmed compromised user or pivot host the model left out. It writes the rules to a blocklist table, the simulated attack traffic stops, and only then does it write the incident report, which is saved to

 Guild.ai
 ClickHouse