Aegis is an on-call assistant for security teams. When an attack shows up in live traffic, it investigates, proposes a fix, and speaks a short briefing. Nothing is deployed until a person clearly approves it by voice.
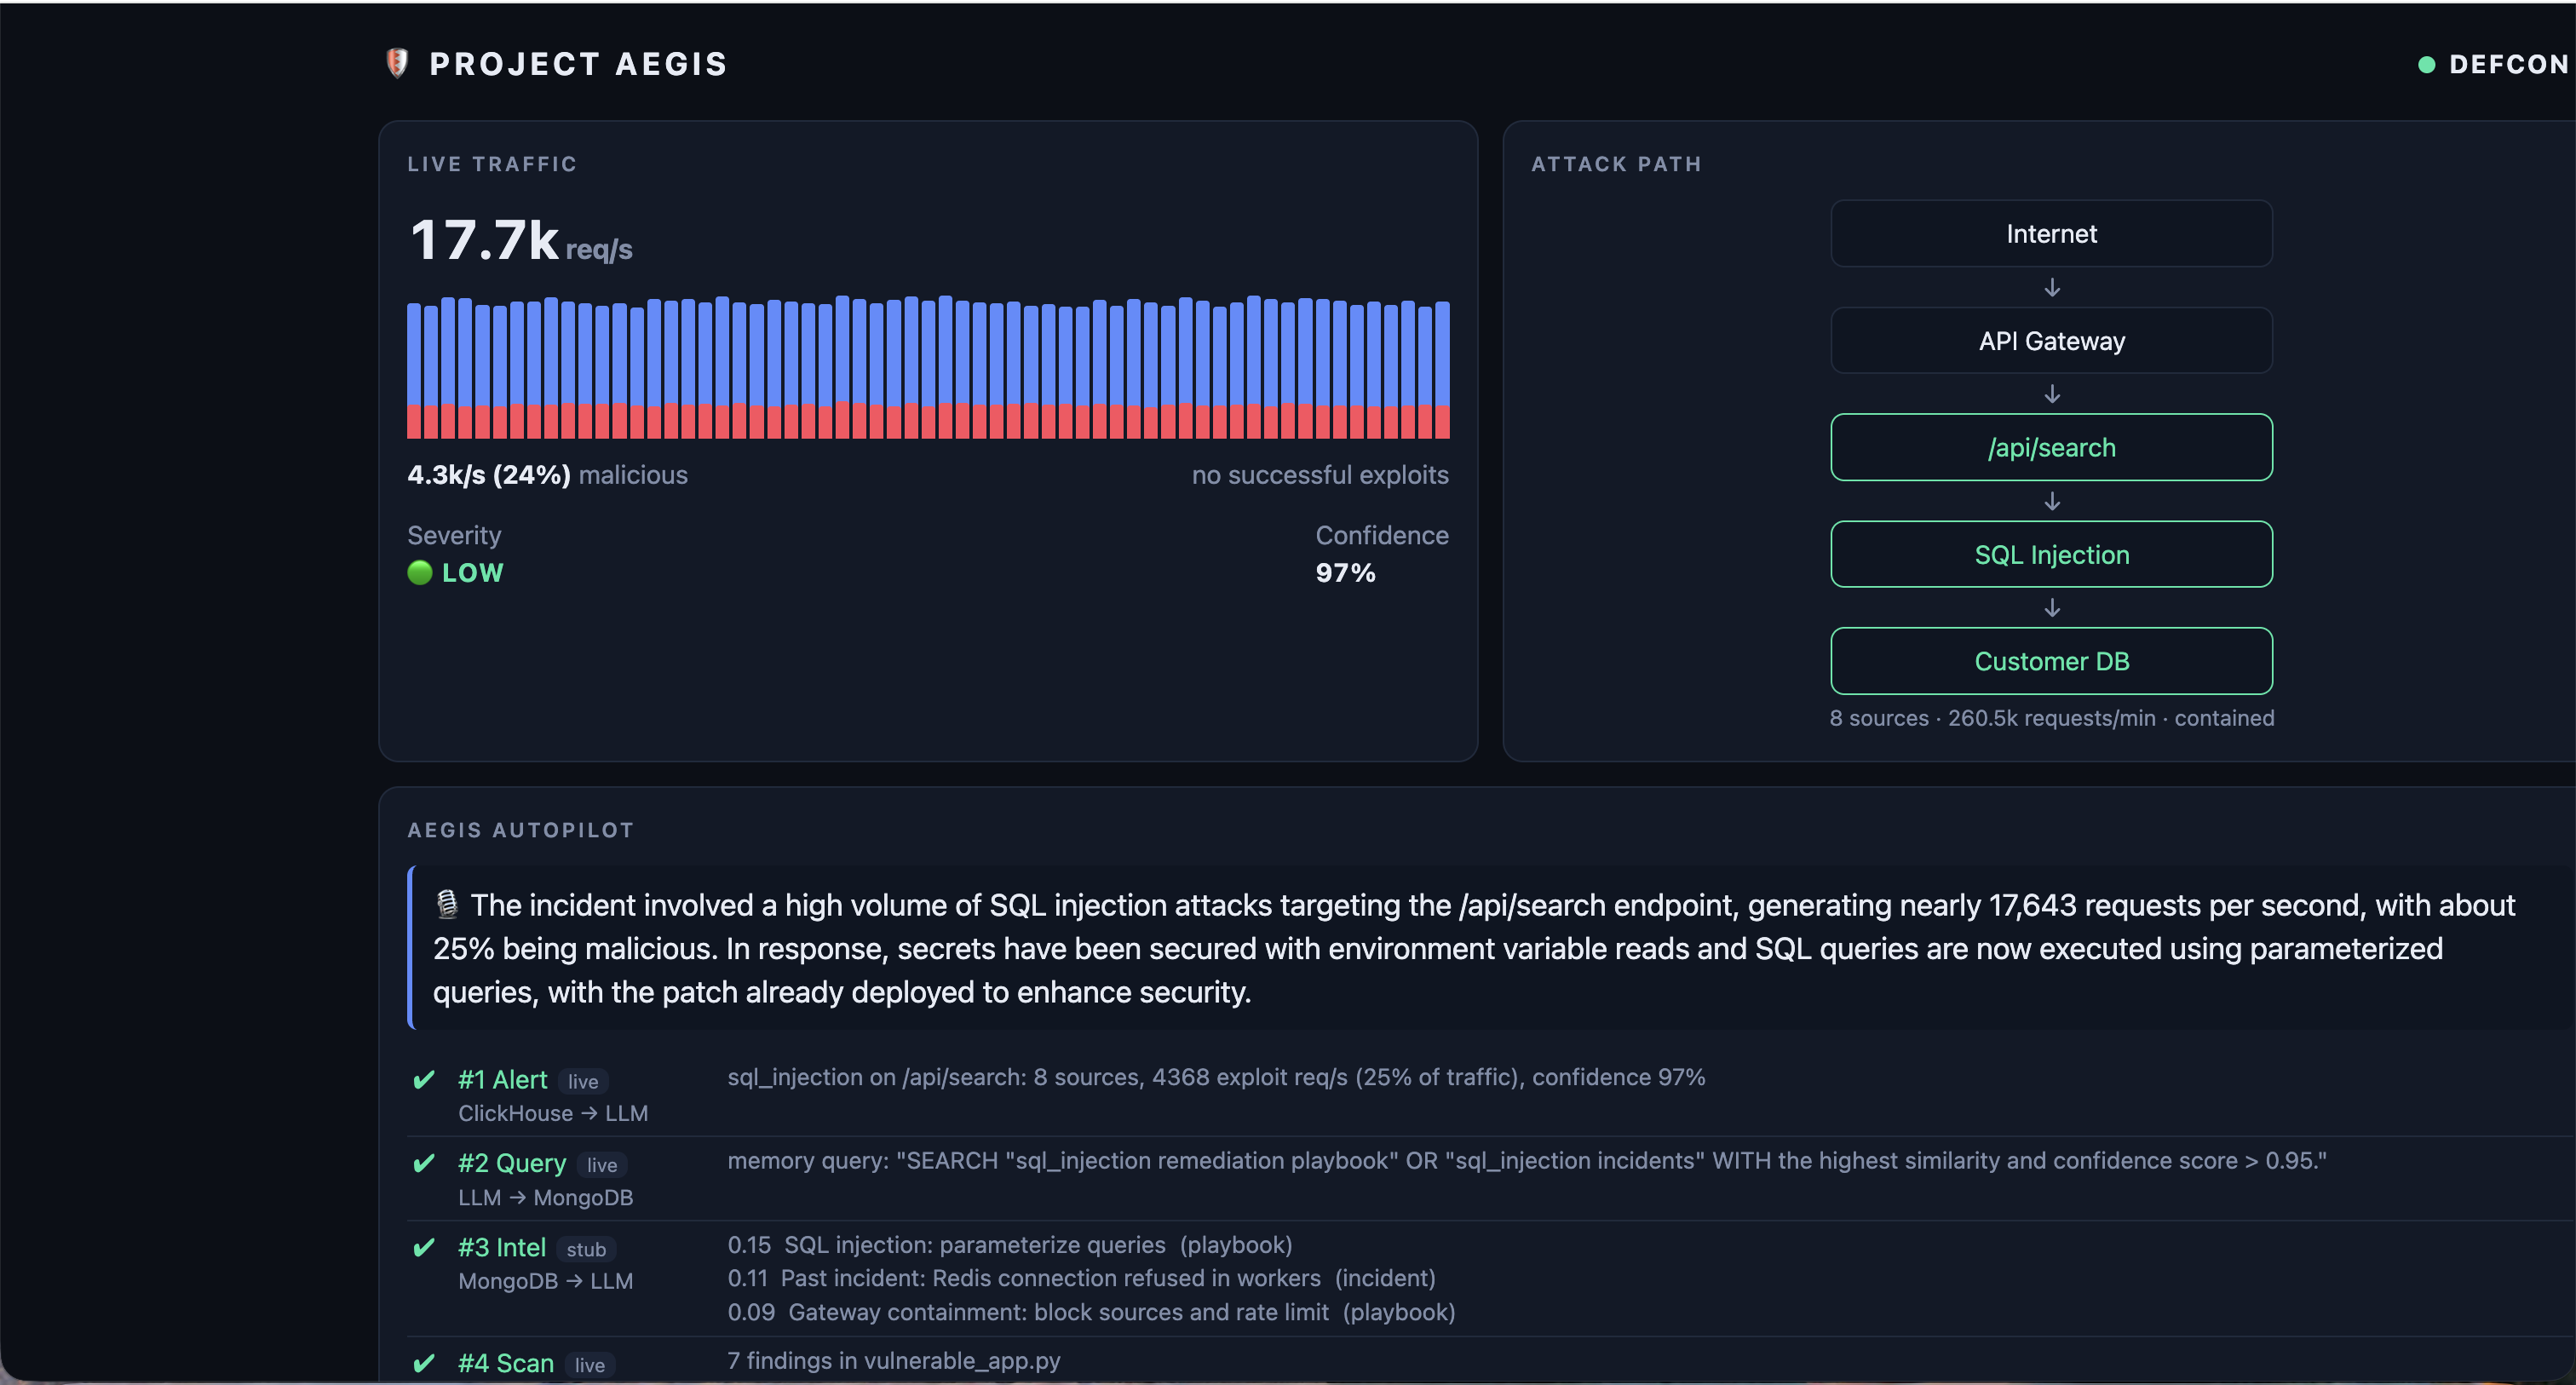
ClickHouse flags an active SQL injection. Aegis pulls matching playbooks and past incidents from MongoDB, a Semgrep scout scans the vulnerable code, and a model writes a patch that Semgrep checks again. ElevenLabs reads the briefing aloud. The operator says “approve,” the server checks those words, and only then are attacker IPs blocked and the exploit replayed to confirm it fails. A live dashboard shows the traffic, the attack path, the log evidence, and whether the patch and health checks passed.
It is for the person on call who needs to understand an incident and authorize a response without jumping between tools. Remediation in this demo is simulated, so the prototype never changes real infrastructure.

 ClickHouse