AI agents now browse the web, read files, and hold real credentials. One poisoned page can turn them against you through indirect prompt injection, and they misuse legitimate tools and valid tokens, so traditional tools see normal traffic.
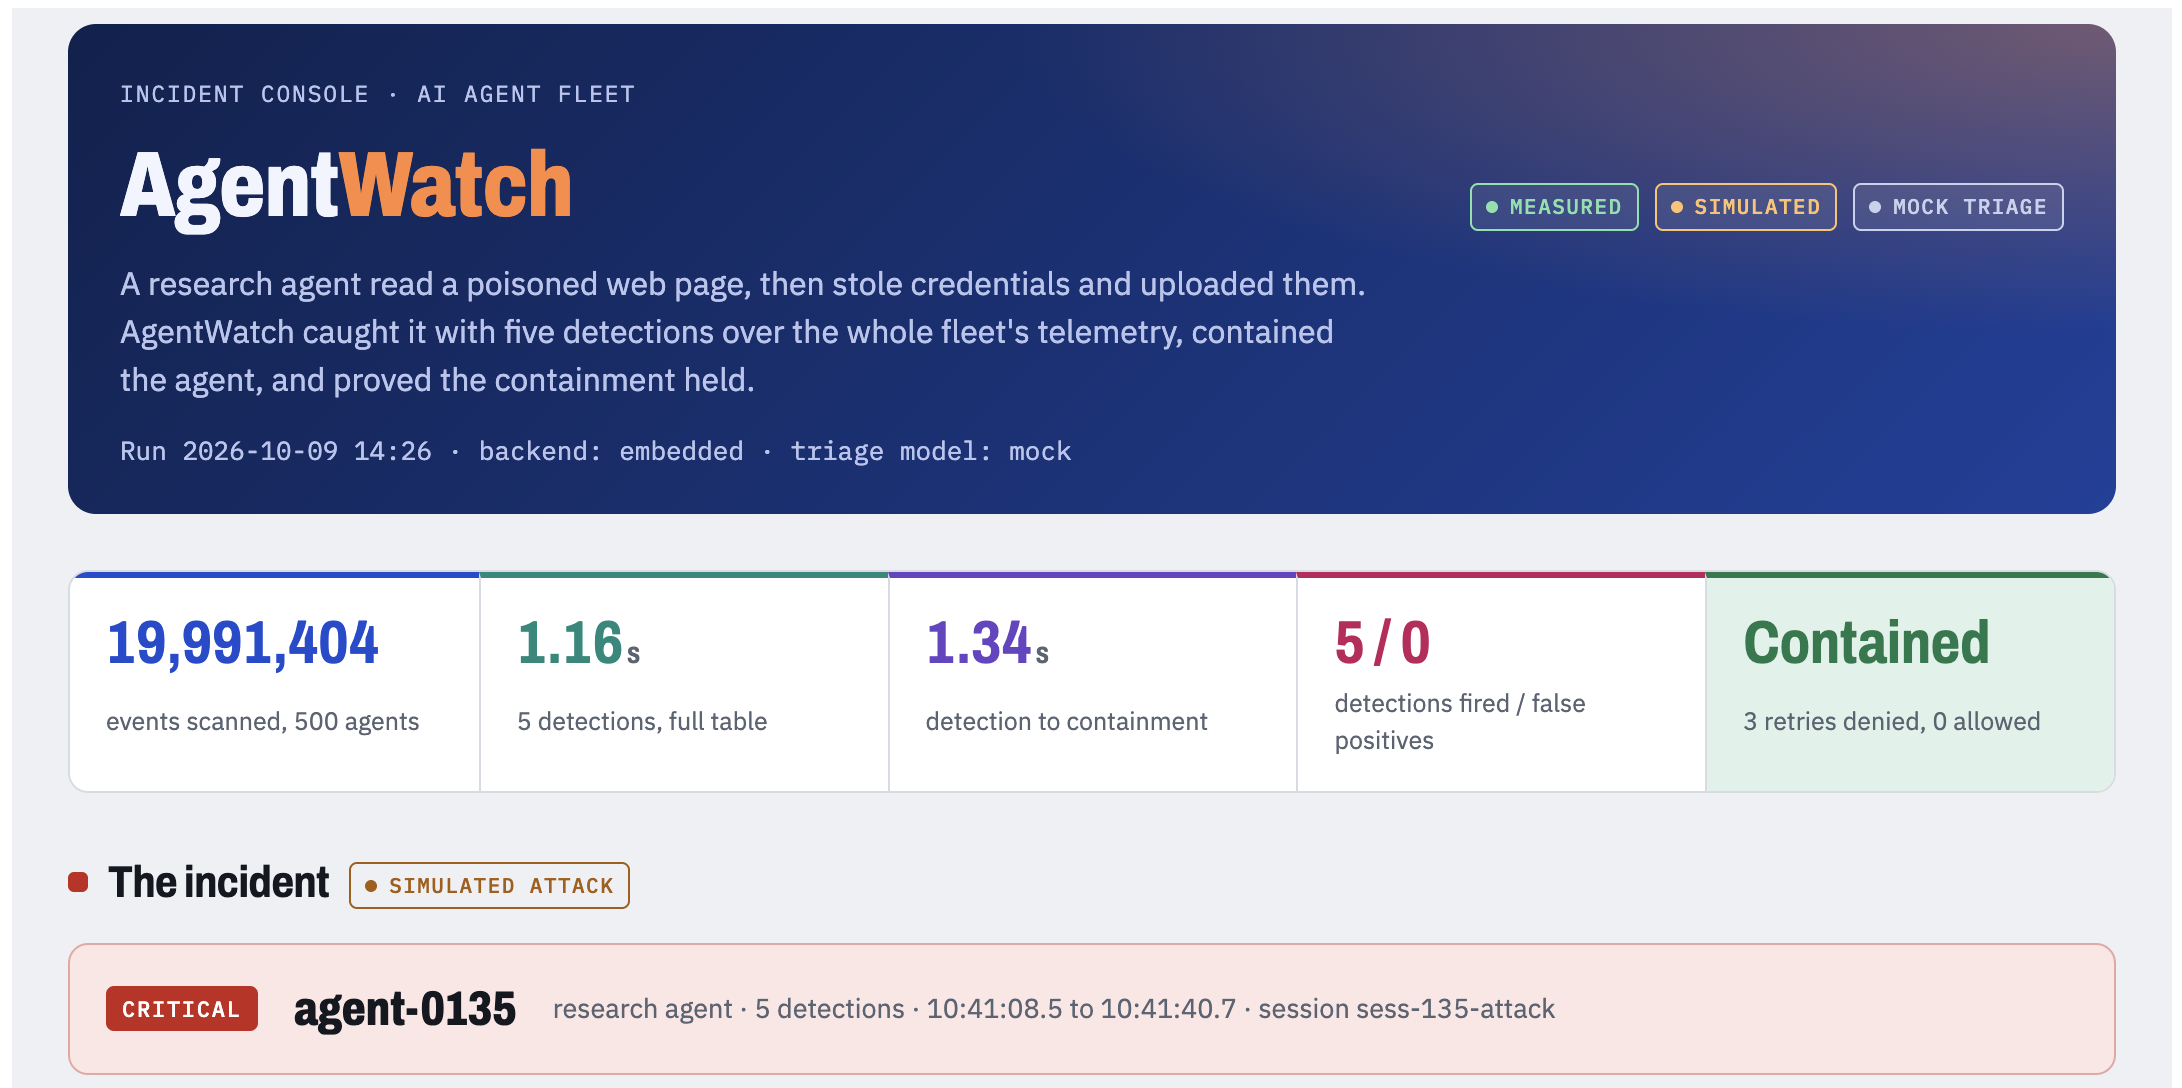
AgentWatch streams every agent action (tool calls, file reads, network requests, credential use) into ClickHouse. Five detection-as-code rules, each with ATT&CK mapping and must-fire/must-not-fire tests, scan 20M events in about 1.2 seconds. They catch an agent that steals AWS and SSH keys, hits the cloud metadata service, uses an admin token, and exfiltrates data, with zero false positives against decoys.
AgentWatch then revokes the token, quarantines the session, and blocks the exfil host, and verifies containment by query: 3 of 3 retries denied.
While building LLM-powered hunting, I found ClickHouse query-level readonly can be overridden within the same query. The guardrail is layered (validation, row limit, locked read-only user), with a custom Semgrep rule flagging the pattern.
Built with ClickHouse (embedded via chDB), Python, pytest, Semgrep, Streamlit. Voiceover by ElevenLabs. Telemetry and attack are simulated for reproducibility; LLM triage is an OpenAI-compatible layer shown in labeled mock mode.

 ClickHouse
 ElevenLabs