tokens&
BrowseFor enterprises
tokens&

Find tools, check provider offers, save a build plan, and share your work when you’re ready.

For buildersFor enterprises

For builders

  • Product launches
  • Builder projects
  • Startup credits and perks
  • Agent Skills
  • Published agents
  • API and agent docs
  • Publish a project

For enterprises

  • Start free company workspace
  • Submit a tool, product, or perk

Community

  • Community
  • Newsletter
  • Events
Xin

© 2026 tokensand, LLC. All rights reserved.

  • Terms
  • Privacy
  • Security
  • Data Processing
  • Status
  1. Hackathon
  2. Project gallery
  3. AgentWatch
Shrutika Joshiabout 1 month agoContributorJudging locked: Event build

AgentWatch

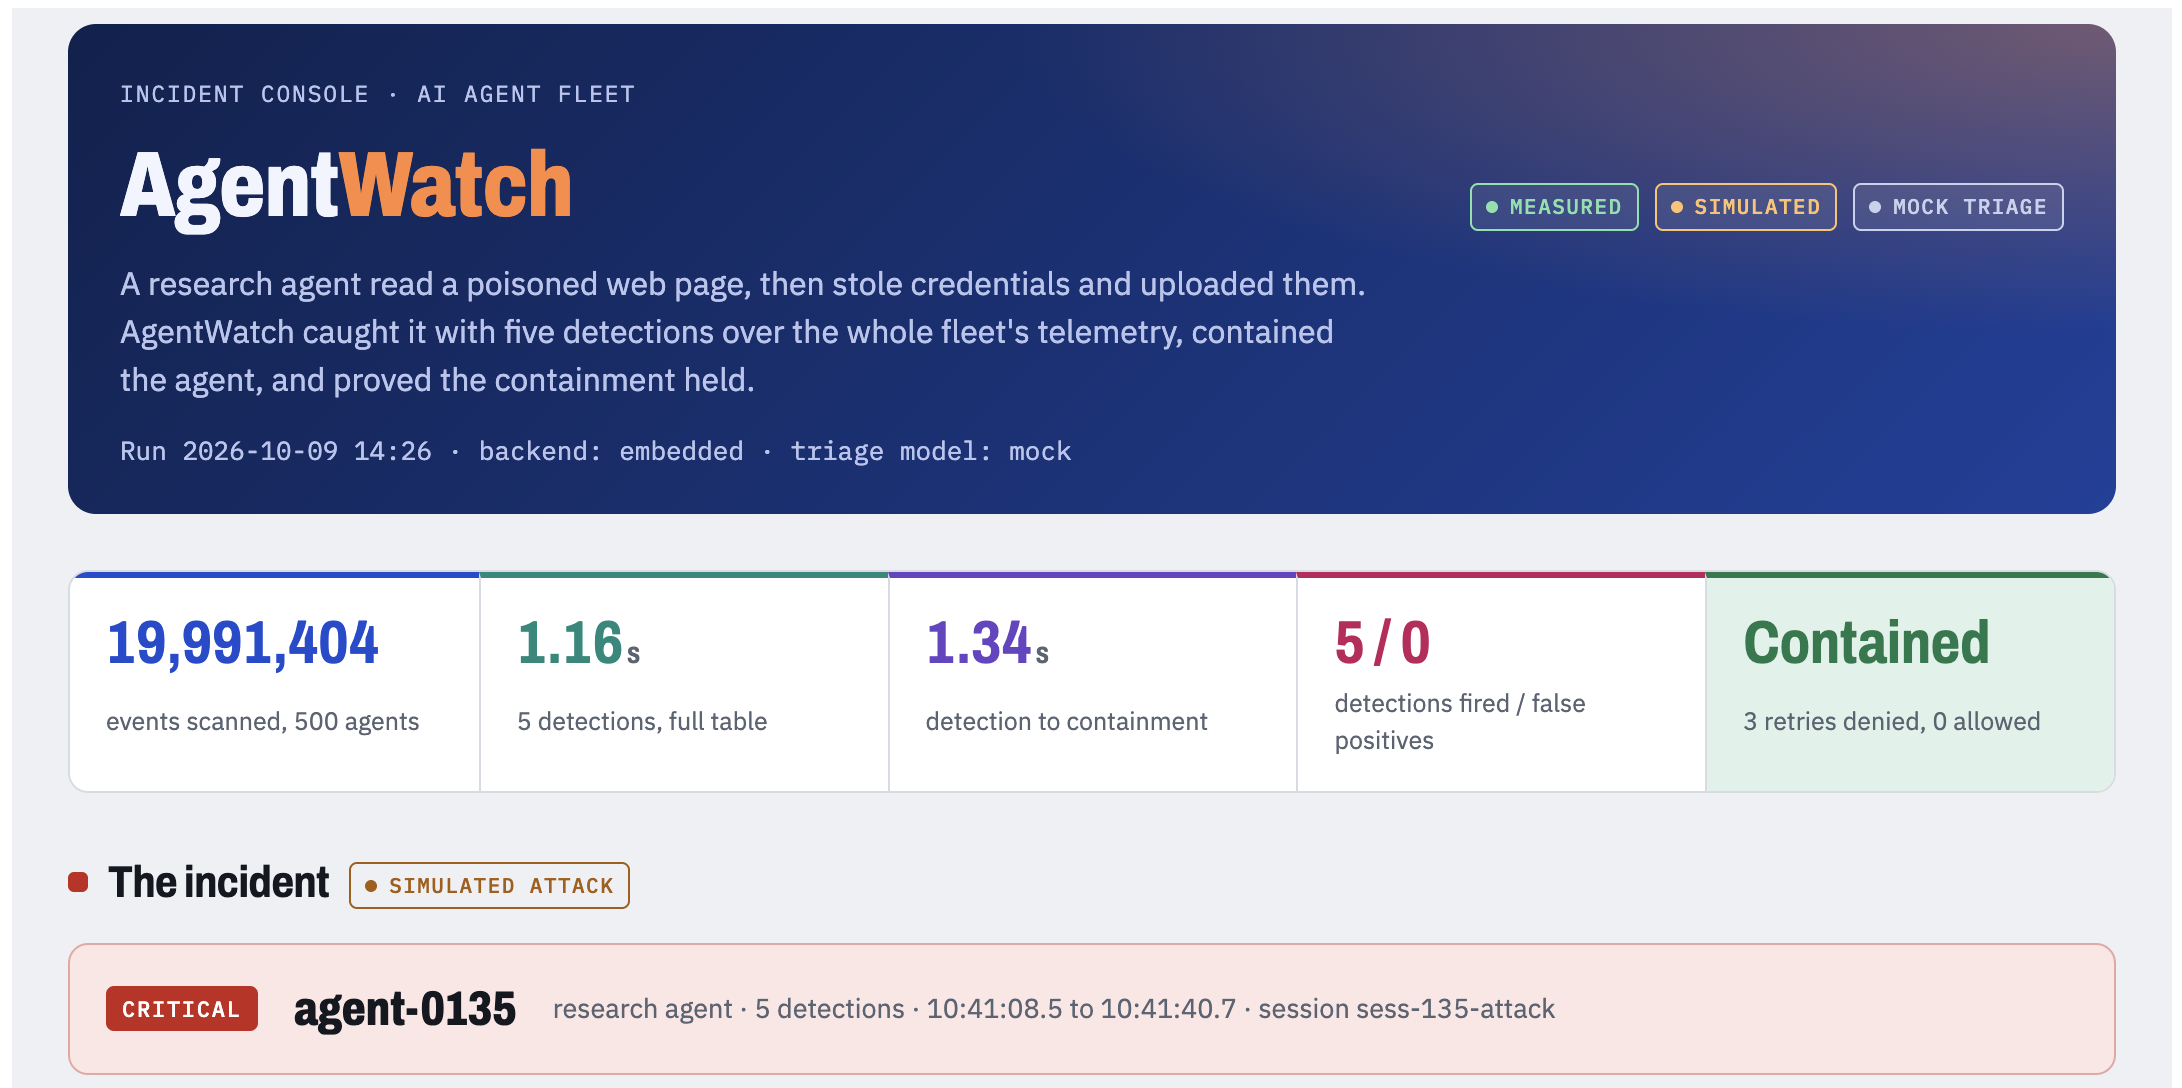
AgentWatch is a SOC for AI agents. It detects an agent hijacked by prompt injection across 20M events in ~1s with ClickHouse, contains it automatically, proves containment held, and guards LLM-written SQL after finding a ClickHouse readonly bypass.

Community votes recognize the build and do not affect official judging.

Review the project

Start with the source code, then open the demo or video if available.

View GitHub repository
Watch demo videoProject gallery
Demo video
Watch demo video
Project description
AI agents now browse the web, read files, and hold real credentials. One poisoned page can turn them against you through indirect prompt injection, and they misuse legitimate tools and valid tokens, so traditional tools see normal traffic. AgentWatch streams every agent action (tool calls, file reads, network requests, credential use) into ClickHouse. Five detection-as-code rules, each with ATT&CK mapping and must-fire/must-not-fire tests, scan 20M events in about 1.2 seconds. They catch an agent that steals AWS and SSH keys, hits the cloud metadata service, uses an admin token, and exfiltrates data, with zero false positives against decoys. AgentWatch then revokes the token, quarantines the session, and blocks the exfil host, and verifies containment by query: 3 of 3 retries denied. While building LLM-powered hunting, I found ClickHouse query-level readonly can be overridden within the same query. The guardrail is layered (validation, row limit, locked read-only user), with a custom Semgrep rule flagging the pattern. Built with ClickHouse (embedded via chDB), Python, pytest, Semgrep, Streamlit. Voiceover by ElevenLabs. Telemetry and attack are simulated for reproducibility; LLM triage is an OpenAI-compatible layer shown in labeled mock mode.
Project links
  • GitHub repository
  • Demo video
Tools used
  • ClickHouse logoClickHouse

    Event resource · ClickHouse docs

    Sign in to visit
Builder

Shrutika Joshi

Builder on tokens&

  • Semgrep logoSemgrep

    Event resource · Claude Code installation instructions

    Sign in to visit
  • COclaude Opus 5.5
    No link provided
  • ElevenLabs logoElevenLabs
    No link provided