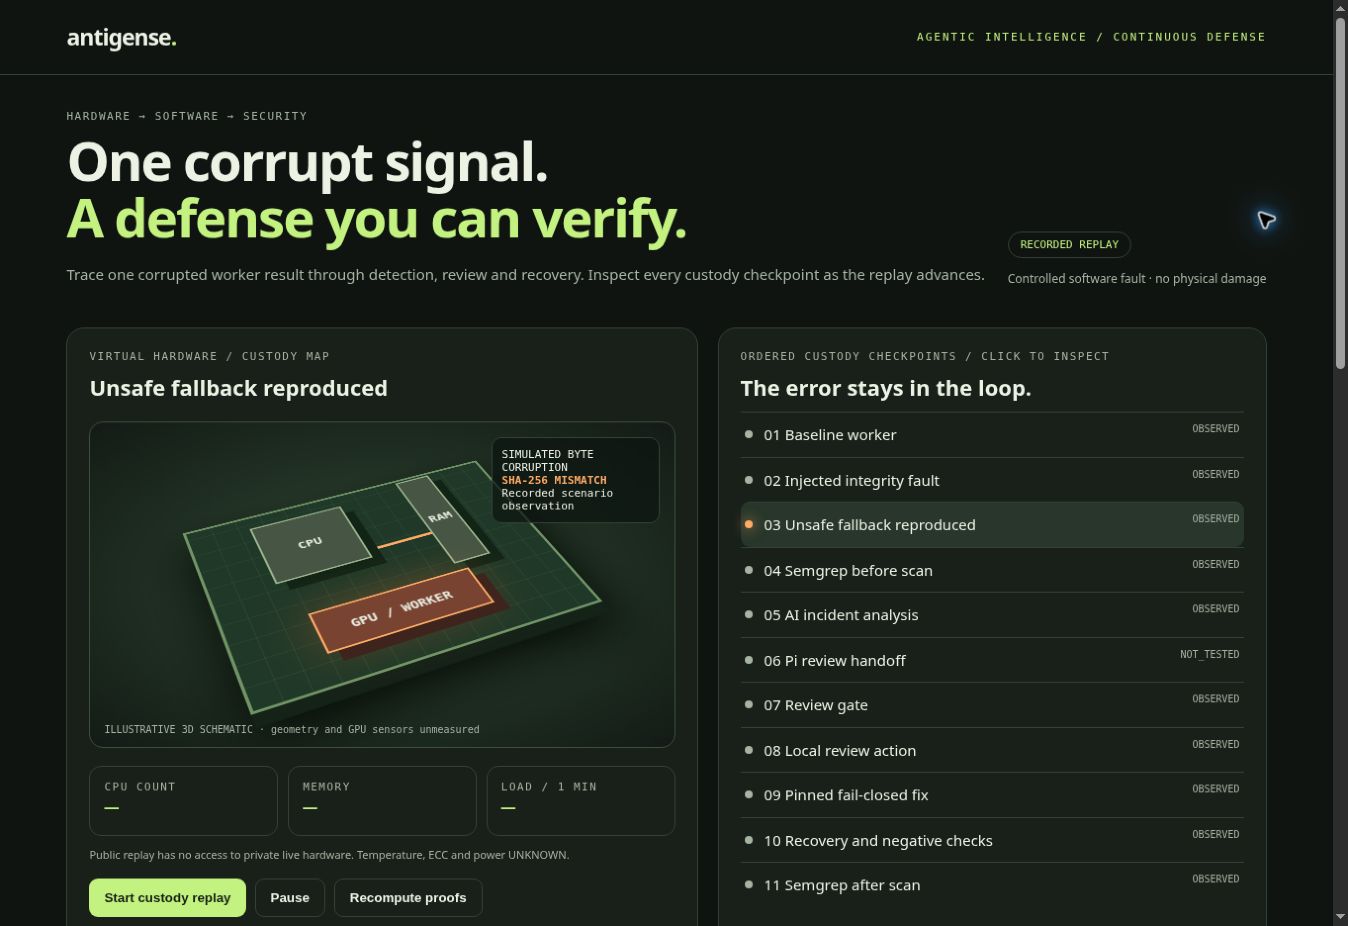
Antigense Daisy is an evidence-driven agentic cyberdefense prototype. A controlled worker-byte fault exposes a fail-open authorization fallback. Semgrep CE detects the pinned flaw (1 finding before; 0 after). A four-case regression oracle confirms the correction denies unauthorized work while preserving legitimate requests; AI-generated advice never authorizes its own application.
Each recorded transition becomes an addressable Fractal Custody Object (FCO) linked through typed Fractal Custody Graph (FCG) relationships. Ordered Merkle/MMR checkpoints support independent replay and byte-integrity verification. A separate 12-leaf local review execution is browser-verifiable.
Executed sponsor evidence: Semgrep local scans; Akash GPU deployment and Qwen2.5:0.5b inference (HTTP 200, 3,466.4 ms), followed by a successful close request; and ClickHouse Cloud ingestion/replay with 55 exact historical readbacks. An earlier Akash HTTP 401 failure remains preserved.
Successor 050 adds a live LOCAL judge cockpit: ALLOW/DENY reviews append FCOs/MMR roots; spectators receive redacted SSE updates; private notes require local authorization. All 17 local tests passed, including unauthorized, cross-origin, stale-root and tamper controls.
Local 050 is NOT remotely hosted and does NOT re-run sponsor cloud APIs. Judge identity, hardware/TEE attestation, Pi execution, real payments and financial ROI are unverified. Hashes establish byte integrity, not truth or causality.
 Semgrep
 Akash
 ClickHouse
 Tokens&