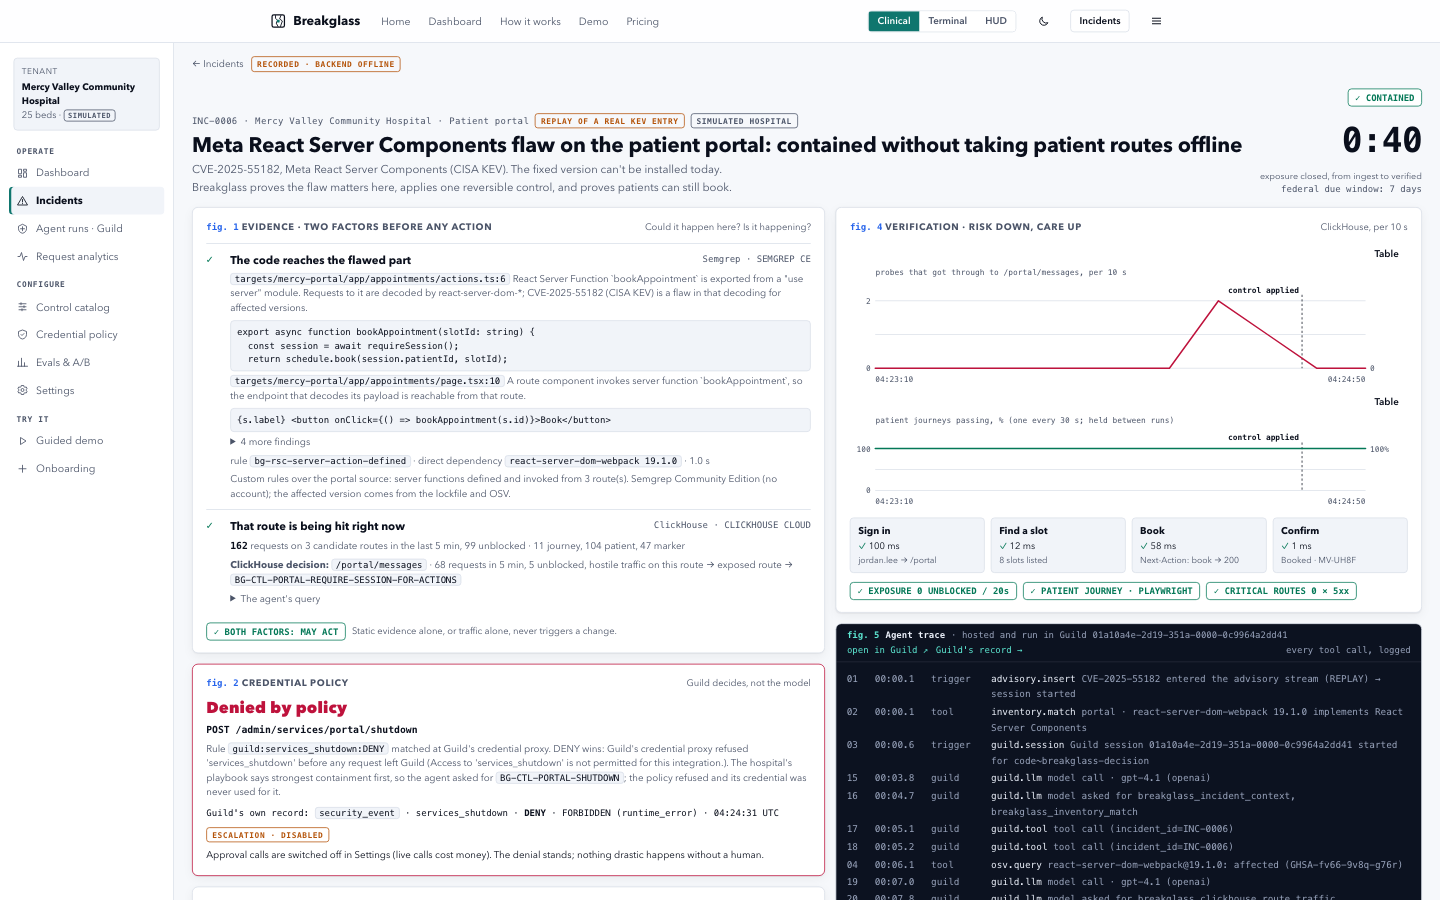
Breakglass buys time when an exploited flaw has no fixed build yet: one pre-approved, reversible control, not a portal shutdown. Simulated hospital; recorded runs.
A real CISA KEV entry opens a case via MongoDB Atlas. Semgrep custom rules flag the relevant code; one grouped ClickHouse query checks current route traffic. The agent, hosted and run on Guild, selects one pre-approved control ID, never rule logic. Guild's credential policy denied services_shutdown in all 6 recorded runs that attempted it; the agent never held the credential. A booking failure triggers automatic rollback.
ClickHouse Cloud: 3,563,922 rows, mostly replayed real public logs. INC-0015's decision query read 8,207 rows in 9.5 ms (server time); contained in 1:26. Each incident has a sourced attack timeline.
Pre-registered A/B on a test twin: 0 of 40 probes through vs 40 of 40 unmanaged; 12 of 12 bookings in both. Recorded containment: 0:40; stale-inventory fault: reverted, contained in 1:03.
Semgrep rule bg-authz-fnmatch-on-raw-path flagged our AI-written credential proxy: fnmatch authorized /admin/controls/BG-CTL-x/../../services/portal/shutdown#/apply while httpx normalized it to the denied shutdown URL (CWE-863). Latent, not reachable from today's flows; reproduced in unit tests, fixed fail-closed, regression-tested and re-scanned clean.
Innovation: evidence before action, credential limits, and booking verification with rollback, not agent confidence.

 Guild.ai
 ClickHouse
 ElevenLabs