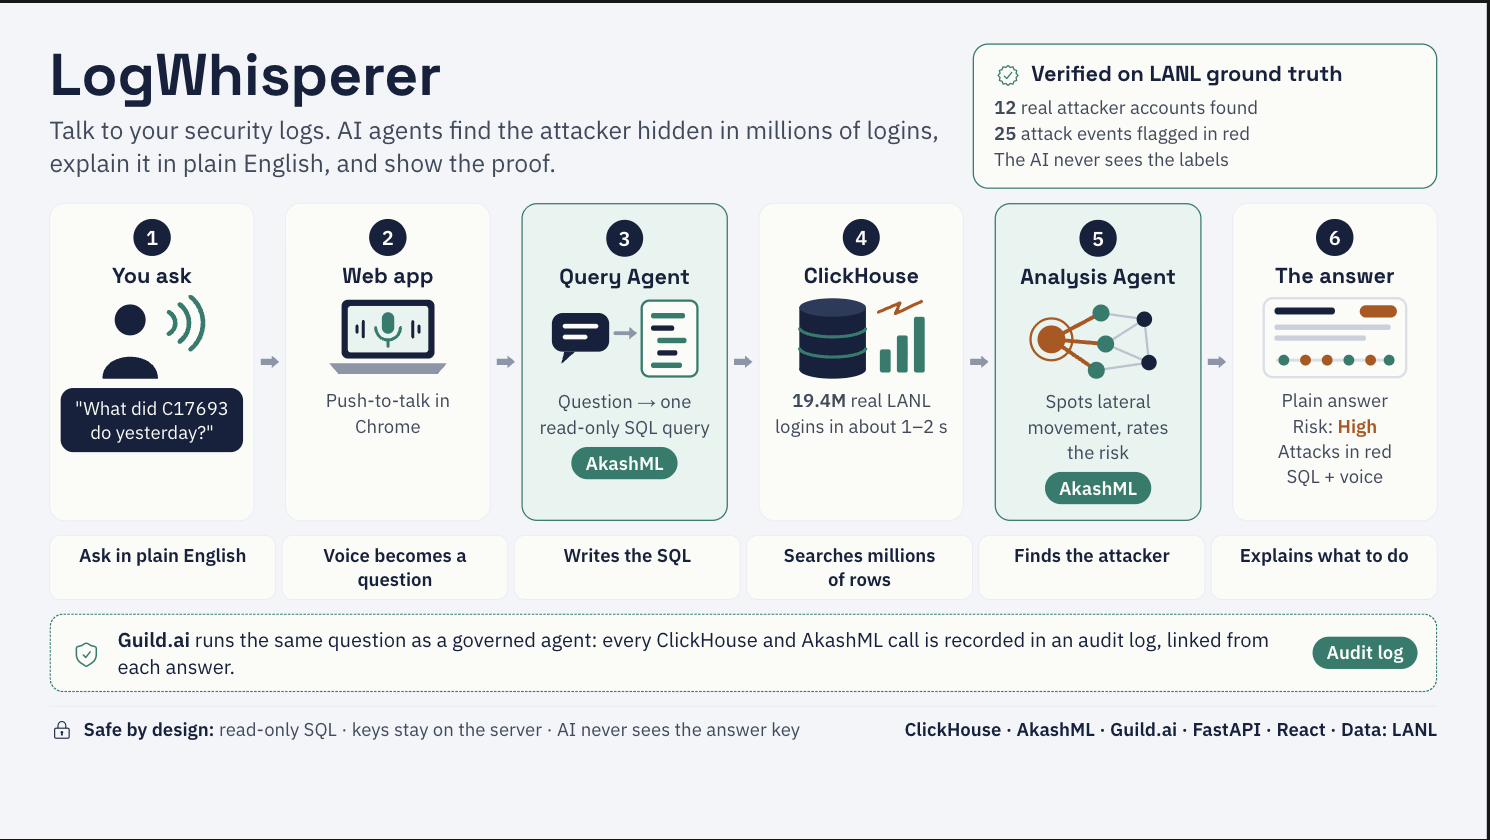
LogWhisperer helps security teams find attackers by asking their logs questions instead of writing query after query. We loaded 19.4 million real login events from Los Alamos National Laboratory's public dataset, recorded during a red-team exercise.
How it works: a spoken or typed question goes to a Query Agent that writes one read-only SQL query. ClickHouse scans the full day of logins in about 1-2 seconds. An Analysis Agent looks for attack patterns like lateral movement, rates the risk, and explains the findings in plain English with next steps. The app shows the answer, a risk badge, an event timeline, the exact SQL, and rows scanned with query time, and can read the answer aloud.
ClickHouse stores the logs and powers every answer; the speed line on screen shows rows scanned and milliseconds.
AkashML runs both agents on the open Kimi-K3 model through an OpenAI-compatible API; after comparing models, we cut answers from about 30 seconds to about 10.
Guild.ai hosts the LogWhisperer agent; every answer links to a Guild session log of each ClickHouse and AkashML call, with credentials kept out of agent code.
Results: checked against LANL's red-team labels, which the AI never sees, it found 12 real attacker accounts on our main question and highlights 25 attack events in red. Safety: a read-only database user, a SELECT-only guard, and keys kept on the server.
 Guild.ai
 ClickHouse