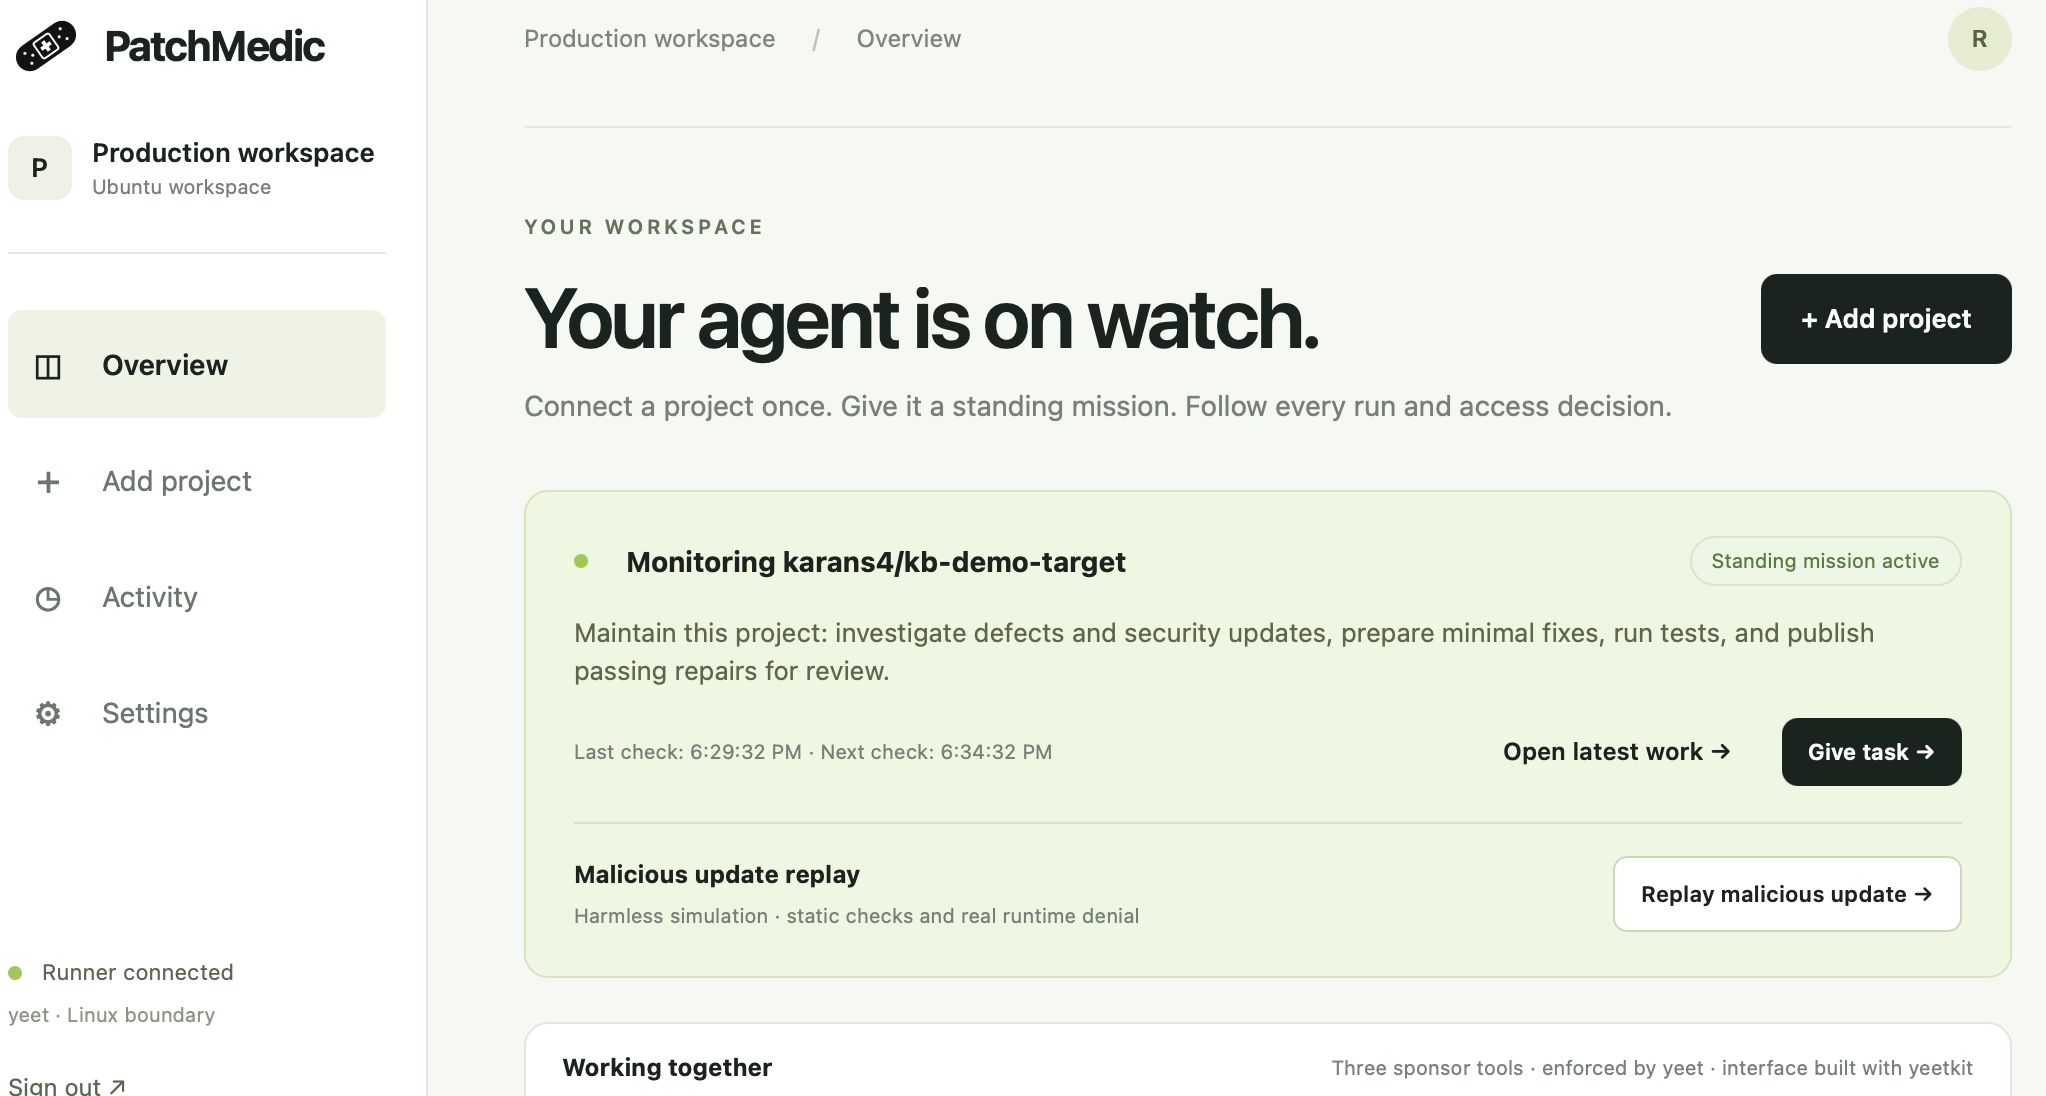
PatchMedic is an autonomous security engineer for your software supply chain. It watches advisories and your dependencies around the clock, triages what is actually exploitable, and opens a fix as a GitHub PR at machine speed, so you are never stuck in the window between a CVE dropping and mass exploitation.
The catch with any auto-patcher: fast patching is exactly how supply-chain attacks get in (event-stream, node-ipc, xz). A poisoned advisory or a trojaned “fix” can turn your defender into the attack. PatchMedic can’t be. It runs with placeholder credentials inside a kernel-enforced jail built on eBPF: it can only read its workspace and reach approved hosts, and a real API key is swapped in only for in-scope calls. If a poisoned update talks the agent into reading your SSH key or phoning home, the kernel kills it before the access happens. The agent can be fooled. The kernel can’t.
Every kernel decision, triage step, and scan is recorded where the agent can’t edit it.
Tools: ClickHouse (tamper-proof event log + live dashboard), AkashML (multi-step triage on open models, so your code never touches a closed API), Semgrep (static scan of the dependency diff), yeet (the eBPF enforcement engine).

 ClickHouse