tokens&
BrowseFor enterprises
tokens&

Find tools, check provider offers, save a build plan, and share your work when you’re ready.

For buildersFor enterprises

For builders

  • Product launches
  • Builder projects
  • Startup credits and perks
  • Agent Skills
  • Published agents
  • API and agent docs
  • Publish a project

For enterprises

  • Start free company workspace
  • Submit a tool, product, or perk

Community

  • Community
  • Newsletter
  • Events
Xin

© 2026 tokensand, LLC. All rights reserved.

  • Terms
  • Privacy
  • Security
  • Data Processing
  • Status
  1. Hackathon
  2. Project gallery
  3. PatchMedic
karanabout 1 month agoContributorJudging locked: Event build

PatchMedic

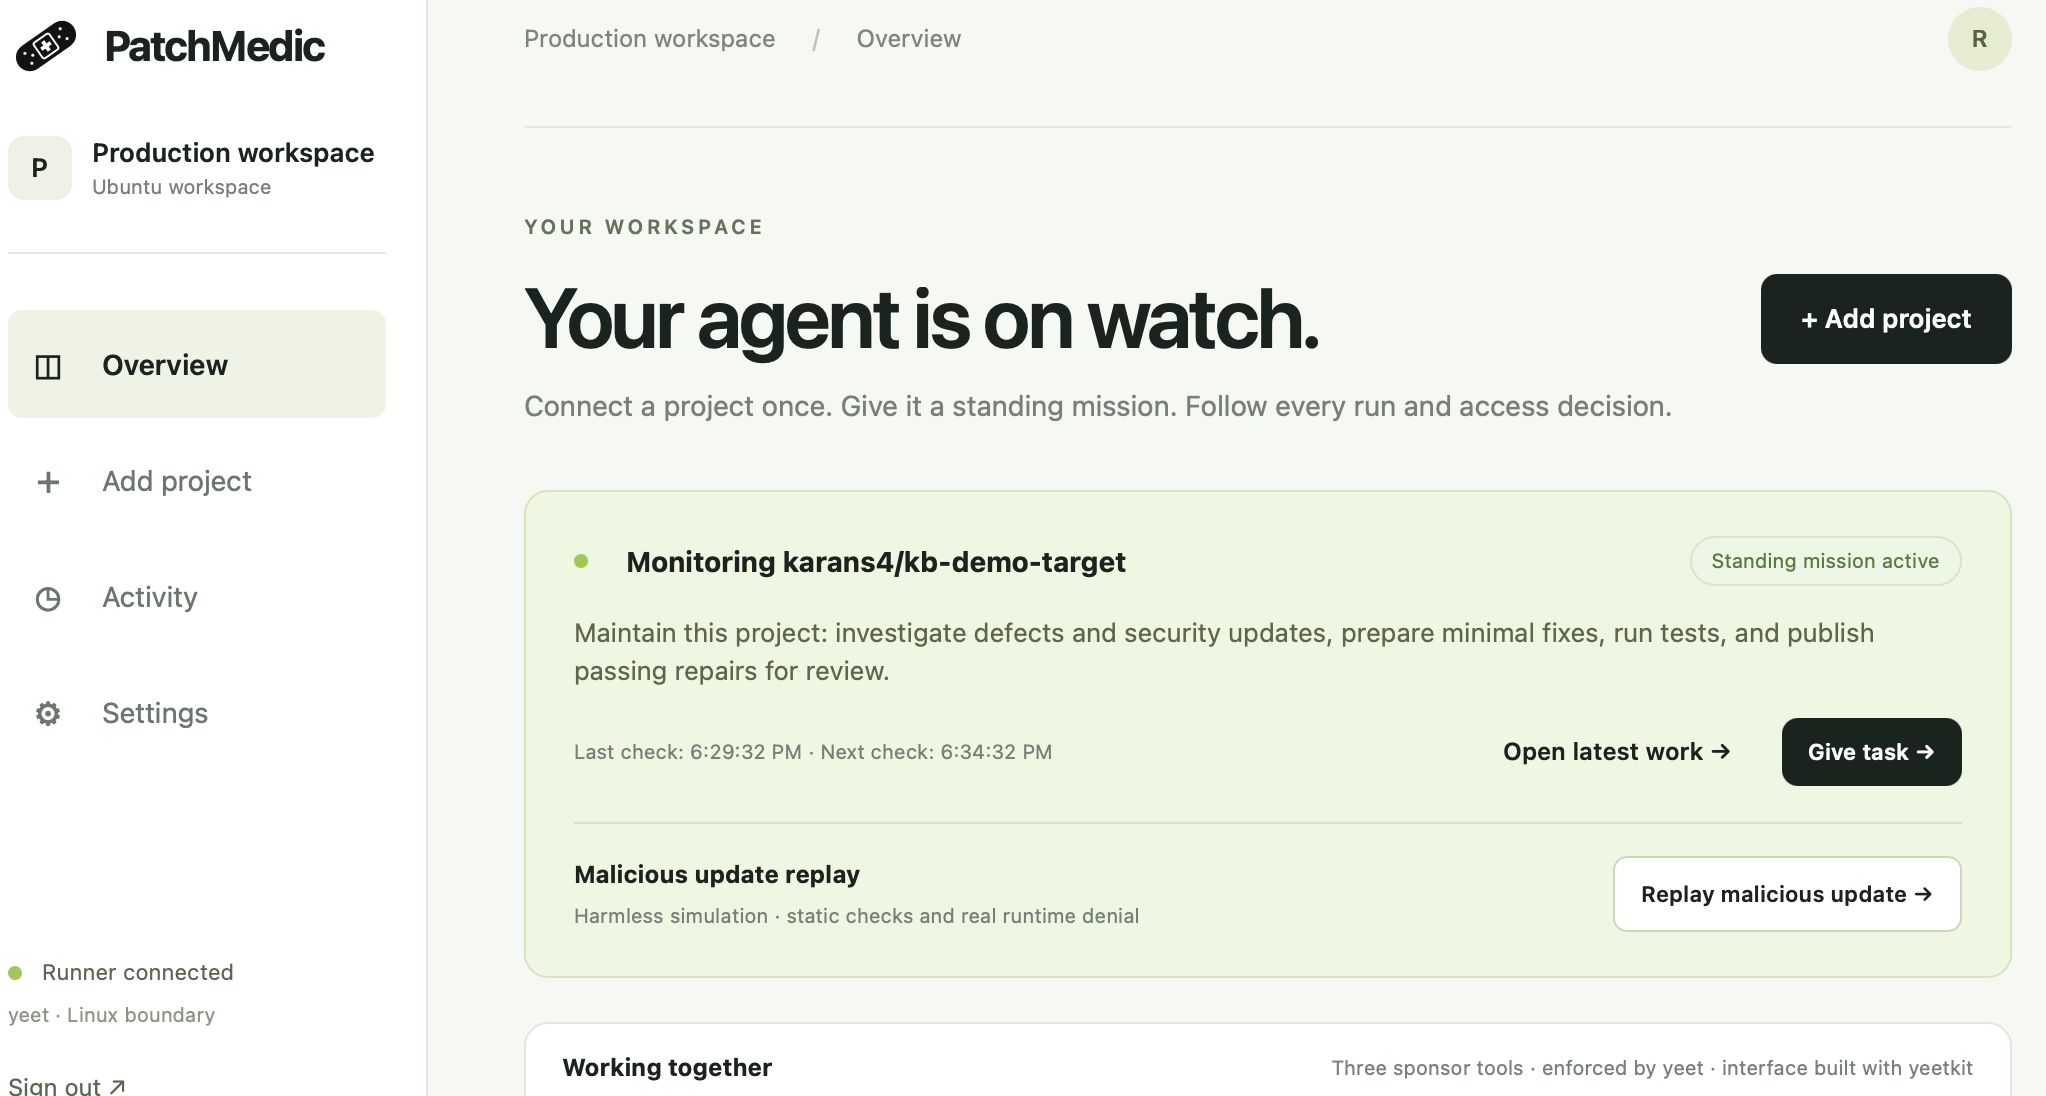
PatchMedic: an autonomous security engineer that can’t be turned into the attack

Community votes recognize the build and do not affect official judging.

Review the project

Start with the source code, then open the demo or video if available.

View GitHub repository
Visit project websiteWatch demo videoProject gallery
Demo video
Watch demo video
Project description
PatchMedic is an autonomous security engineer for your software supply chain. It watches advisories and your dependencies around the clock, triages what is actually exploitable, and opens a fix as a GitHub PR at machine speed, so you are never stuck in the window between a CVE dropping and mass exploitation. The catch with any auto-patcher: fast patching is exactly how supply-chain attacks get in (event-stream, node-ipc, xz). A poisoned advisory or a trojaned “fix” can turn your defender into the attack. PatchMedic can’t be. It runs with placeholder credentials inside a kernel-enforced jail built on eBPF: it can only read its workspace and reach approved hosts, and a real API key is swapped in only for in-scope calls. If a poisoned update talks the agent into reading your SSH key or phoning home, the kernel kills it before the access happens. The agent can be fooled. The kernel can’t. Every kernel decision, triage step, and scan is recorded where the agent can’t edit it. Tools: ClickHouse (tamper-proof event log + live dashboard), AkashML (multi-step triage on open models, so your code never touches a closed API), Semgrep (static scan of the dependency diff), yeet (the eBPF enforcement engine).
Project links
  • GitHub repository
  • Project website
  • Demo video
Tools used
  • ClickHouse logoClickHouse

    Event resource · ClickHouse docs

    Sign in to visit
Builder
KA

karan

Builder on tokens&

  • Pi logoPi
    No link provided
  • Akash logoAkash

    Event resource · Akash docs

    Sign in to visit
  • Semgrep logoSemgrep

    Event resource · Claude Code installation instructions

    Sign in to visit