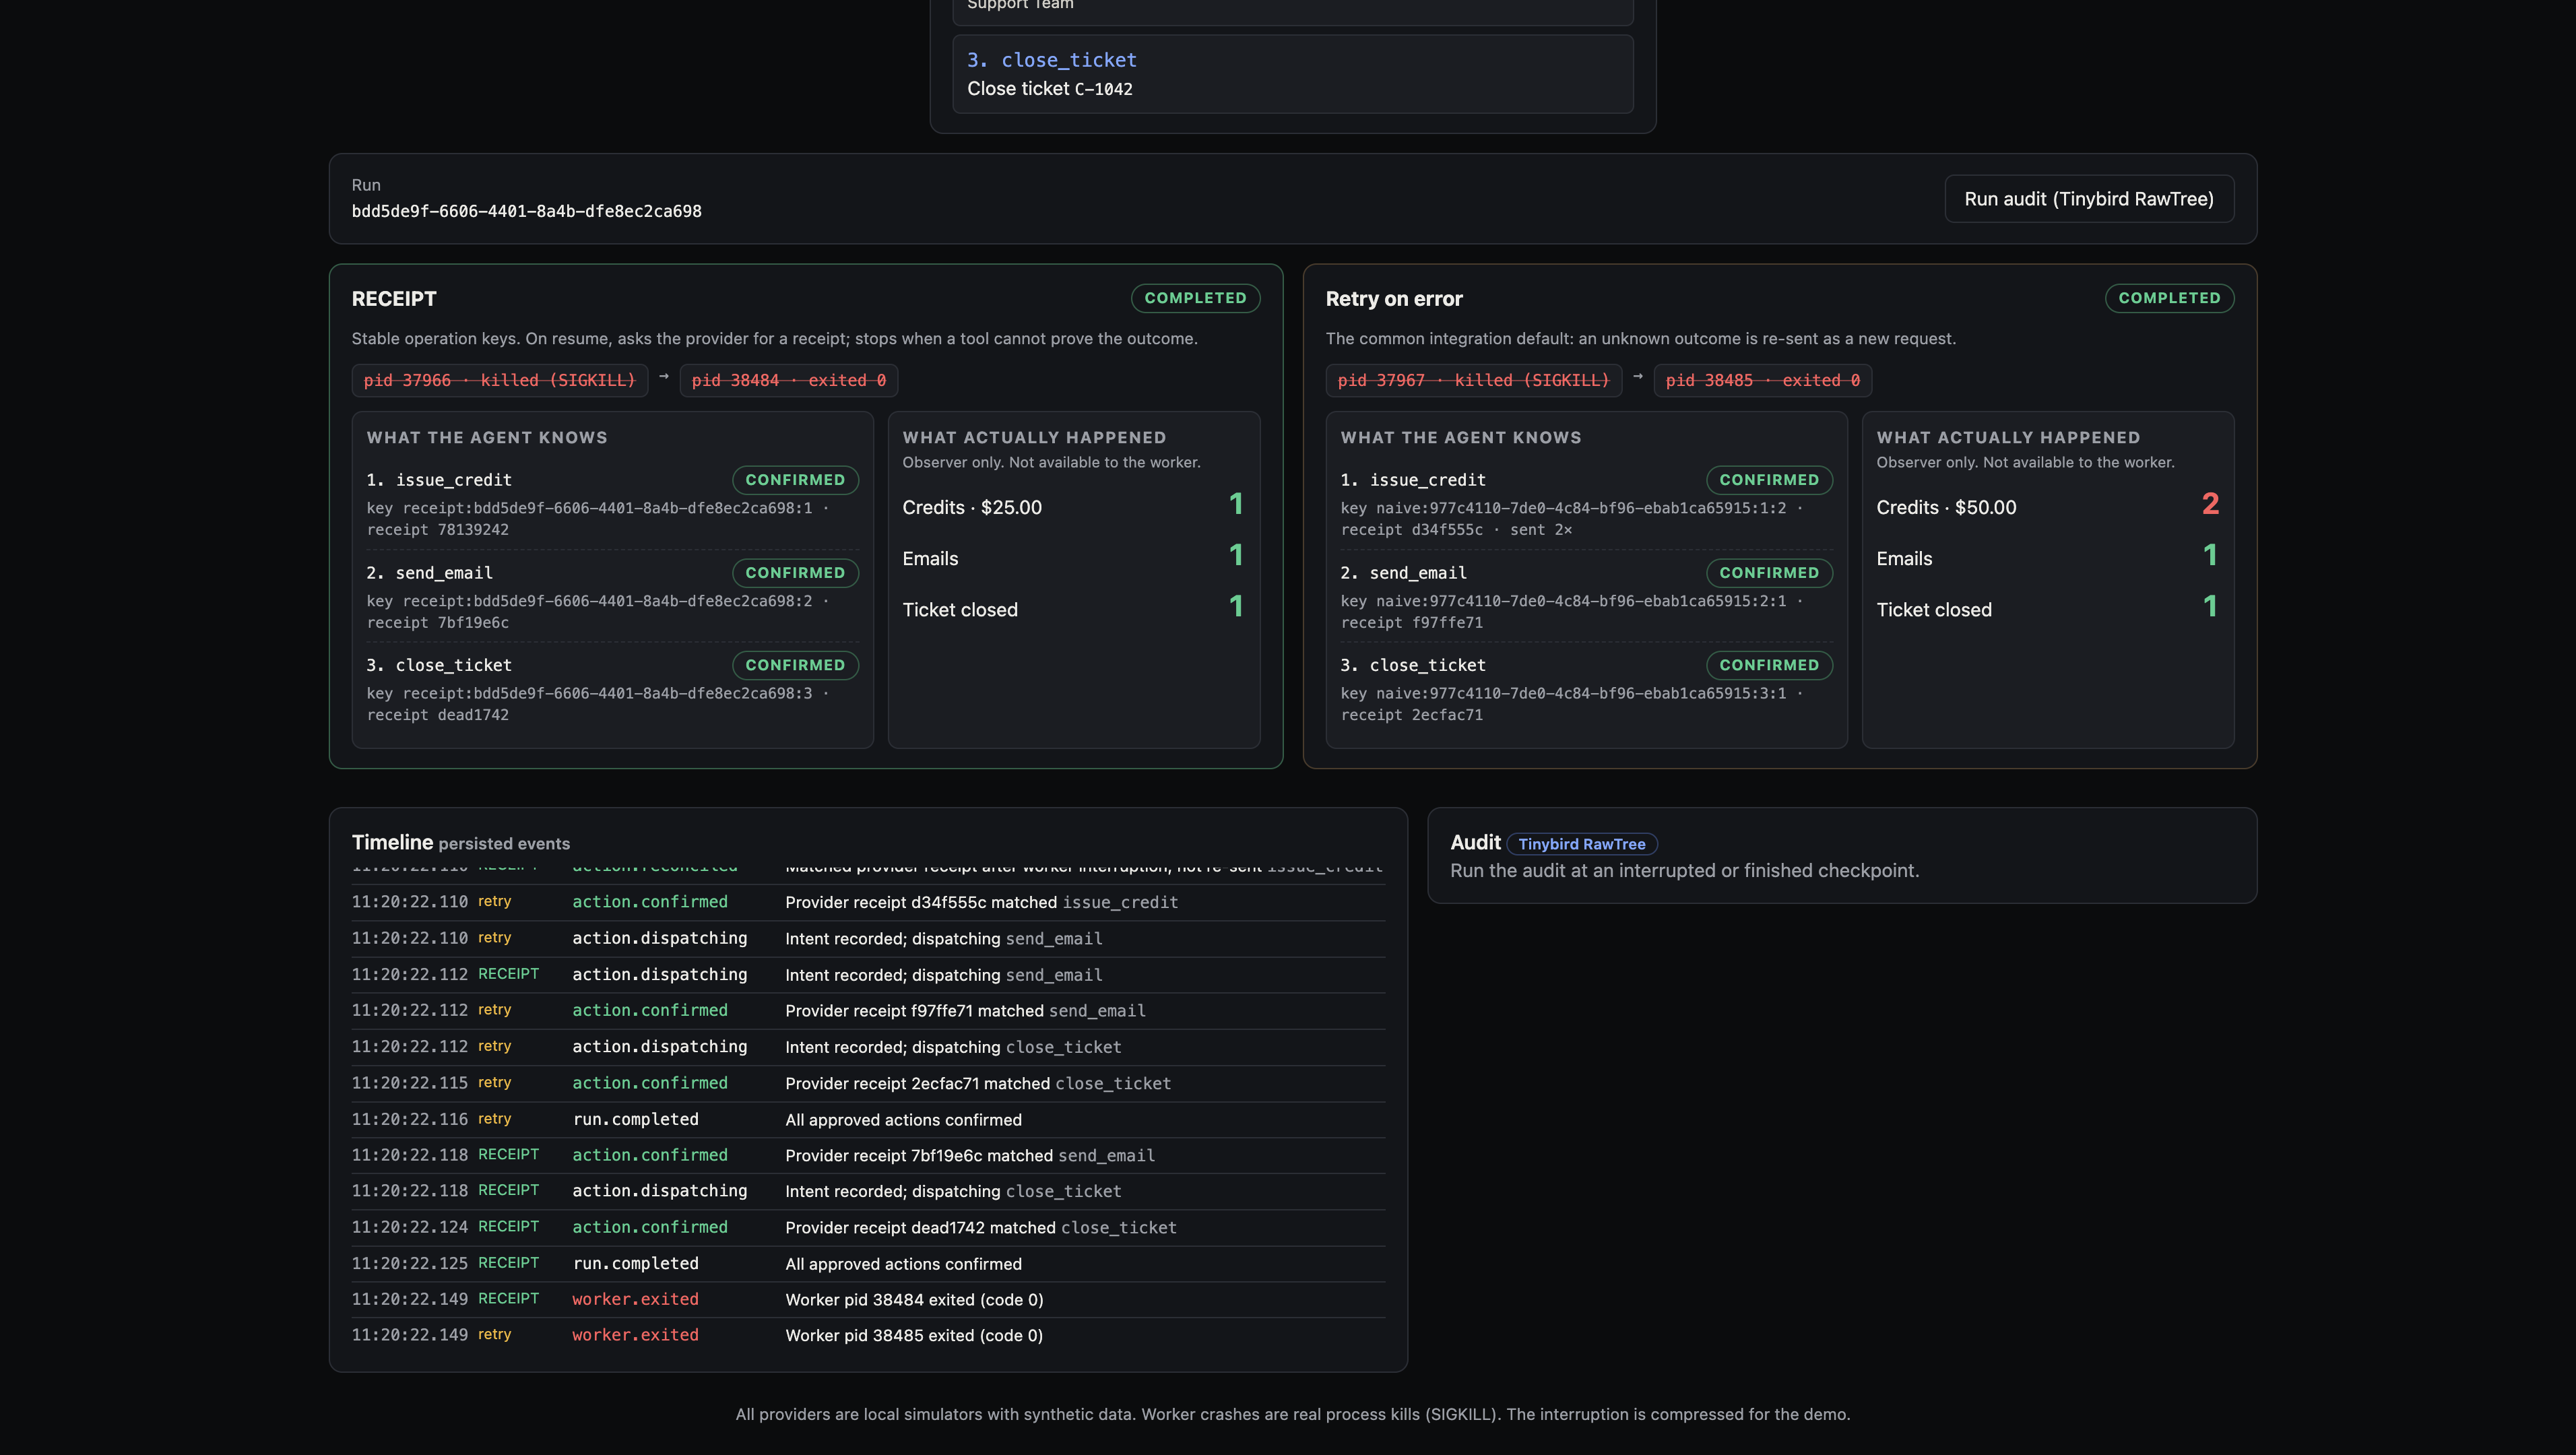
When a support agent crashes mid-refund, it asks for a receipt instead of guessing, so the customer is never (e.g.) credited twice.
Support agents now issue credits, send emails and close tickets. The dangerous moment in a long task: the tool acted, but the agent crashed before hearing back. Memory can't help, because the answer never arrived. A naive retry double-credits the customer.
How it works: every approved action gets a stable operation key, saved before the call. We SIGKILL the worker right after the credit commits. A fresh process resumes from disk, asks the provider for the receipt under that key, and continues only if the tool, key and payload hash match. Each tool is graded Receipt, Idempotent or Blind; with a Blind email tool, RECEIPT stops and writes a handoff note for a human. Side by side, retry-on-error ends at $50 and two emails; RECEIPT ends at one credit, one email, ticket closed. 18 tests, including real process kills.
Tech: Liquid AI LFM2.5 (via OpenRouter) turns the ticket, policy and evidence into a schema-constrained JSON plan, validated in code and approved by a human. Nimble Extract fetches GitHub's real Sept 13 incident page, so the credit rests on evidence. Tinybird RawTree stores every event; the audit query asks "did anything happen twice?" None of them sit on the safety path.
Built from my support and customer success work: before an agent touches a customer's stack, ask which tools are agent-safe.