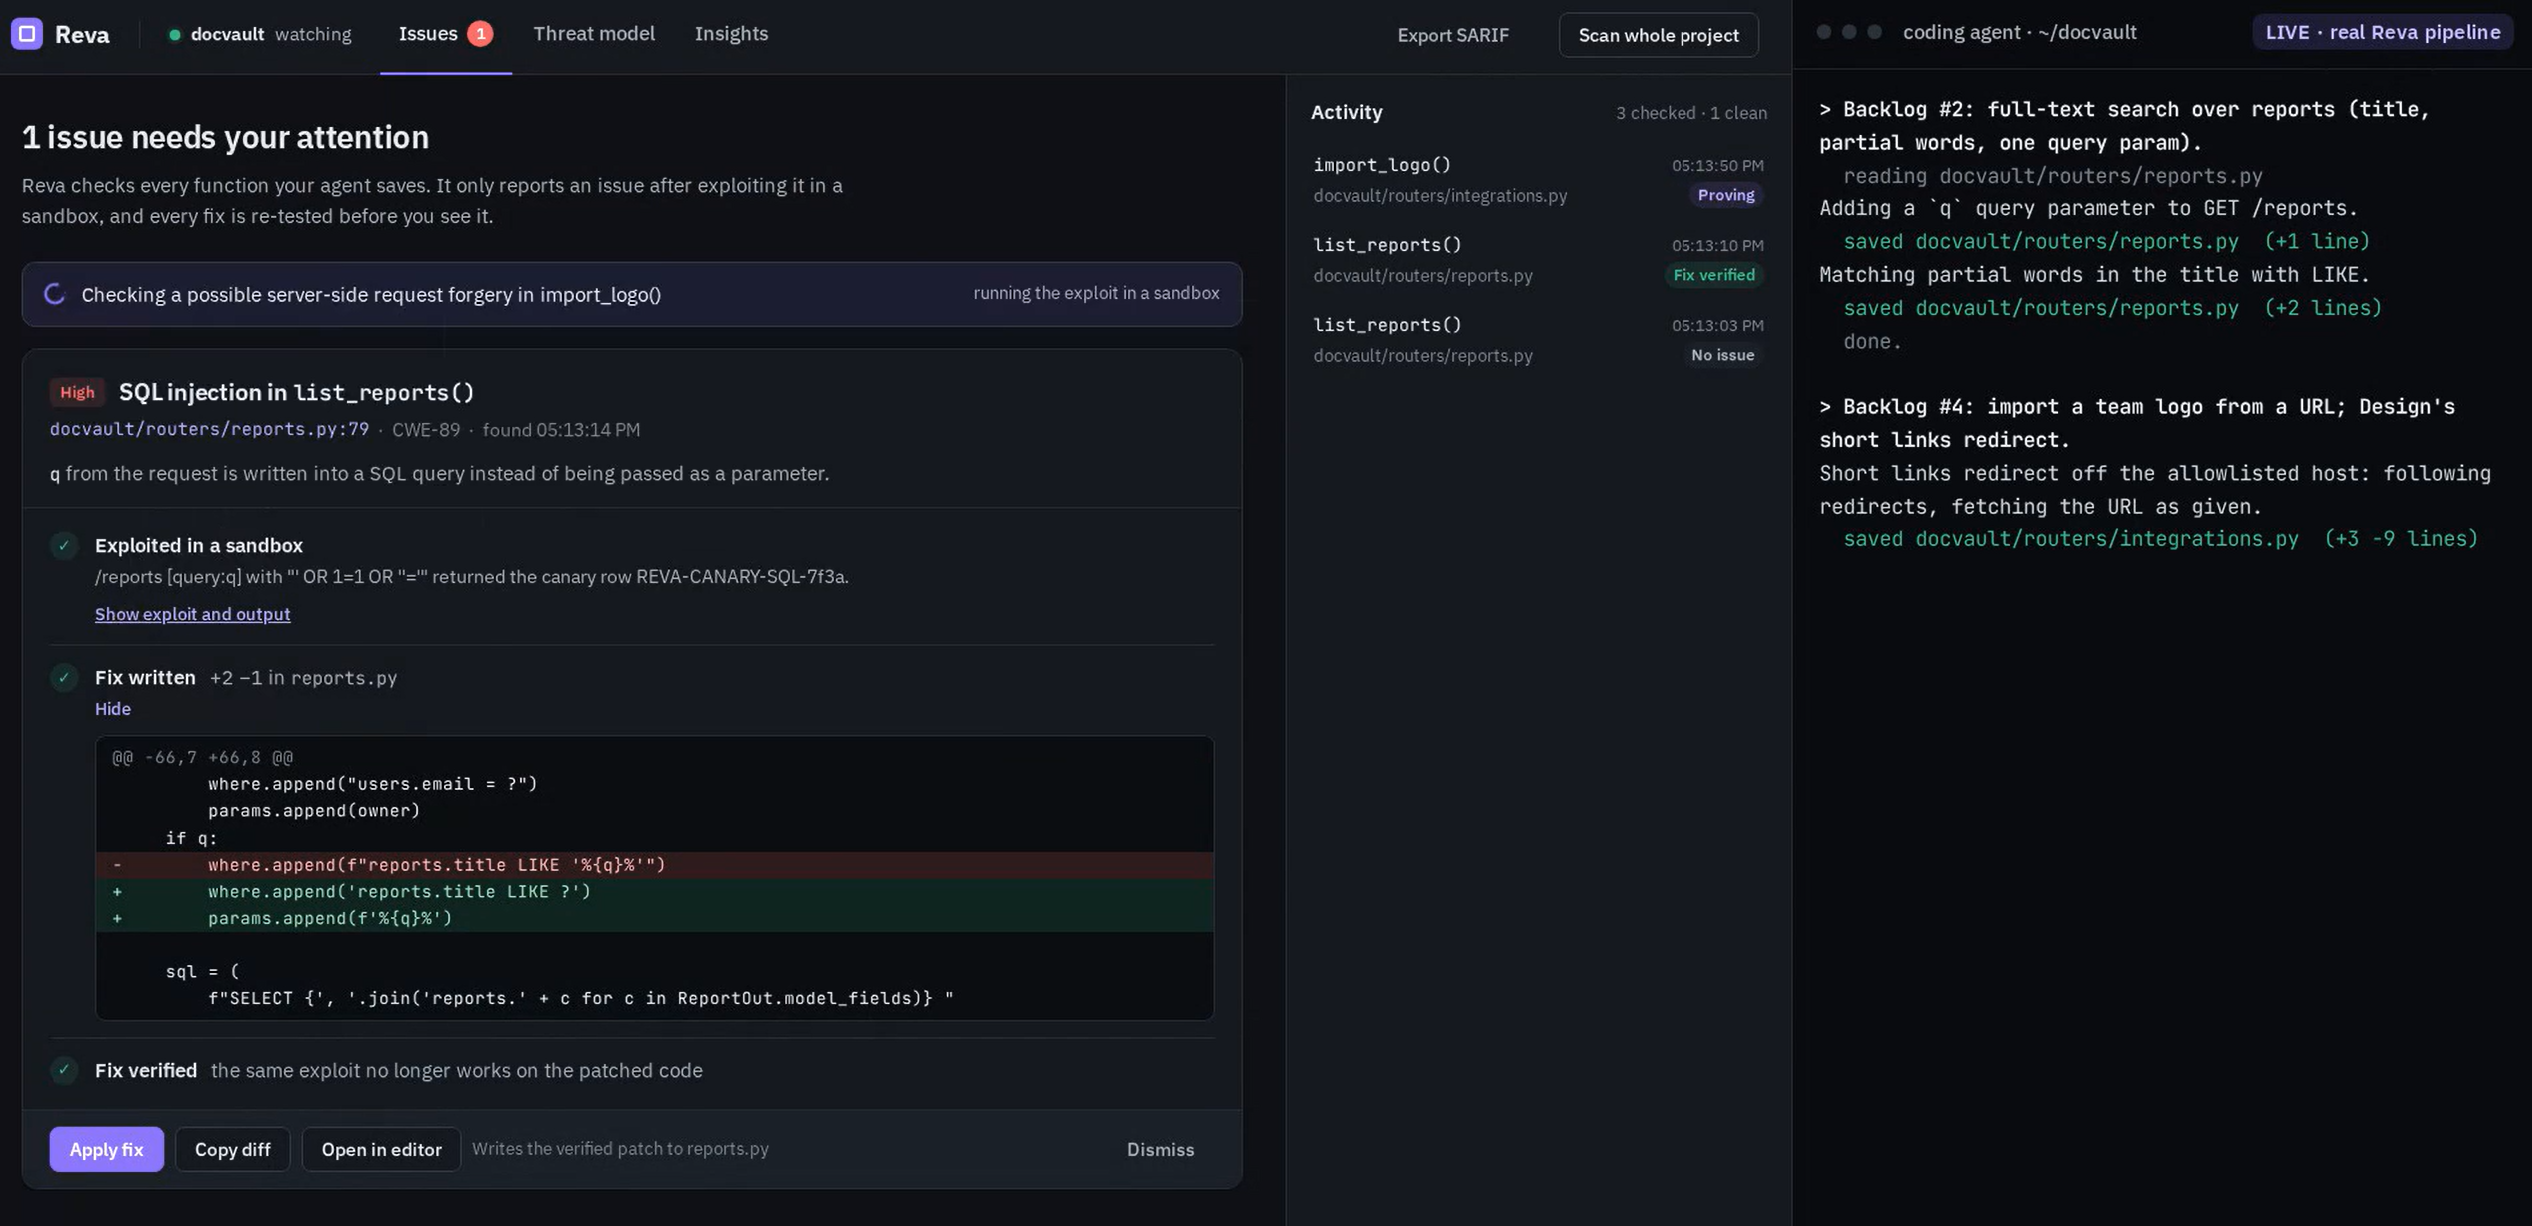
Reva watches a repository while an AI coding agent writes code and reviews every save in seconds. It only raises an issue it can prove, and every issue comes with a verified fix.
Our novel AI detection model:
* Threat-model grounded: data-flow analysis maps untrusted inputs to sensitive operations (SQL, files, outbound HTTP, processes) and records which paths are guarded; an agent review adds assets, trust boundaries and project-specific questions.* Built on top of Semgrep: Semgrep Guardian’s findings on each changed function are packed into the model’s context as evidence, never as the verdict.* Single inference, many questions: one pass answers every screening question at once, and a calibration layer combines the answers with static evidence into a confidence. A free static gate means most saves never reach the model.
Then Reva proves it: suspected issues are checked by running the code in a sandbox with canaries. Only proven issues reach the developer, with a targeted fix re-checked the same way. Results export as SARIF.
Sponsor technologies:
* Semgrep Guardian: the analysis our model builds on.* Akash (AkashML): hosts the model’s transformer, Qwen3.8-27B, for about half a cent per demo run.* ClickHouse Cloud: stores every screening and verdict; the measured hit rate per pattern feeds back into calibration.
* Pi: coding agent

 ClickHouse