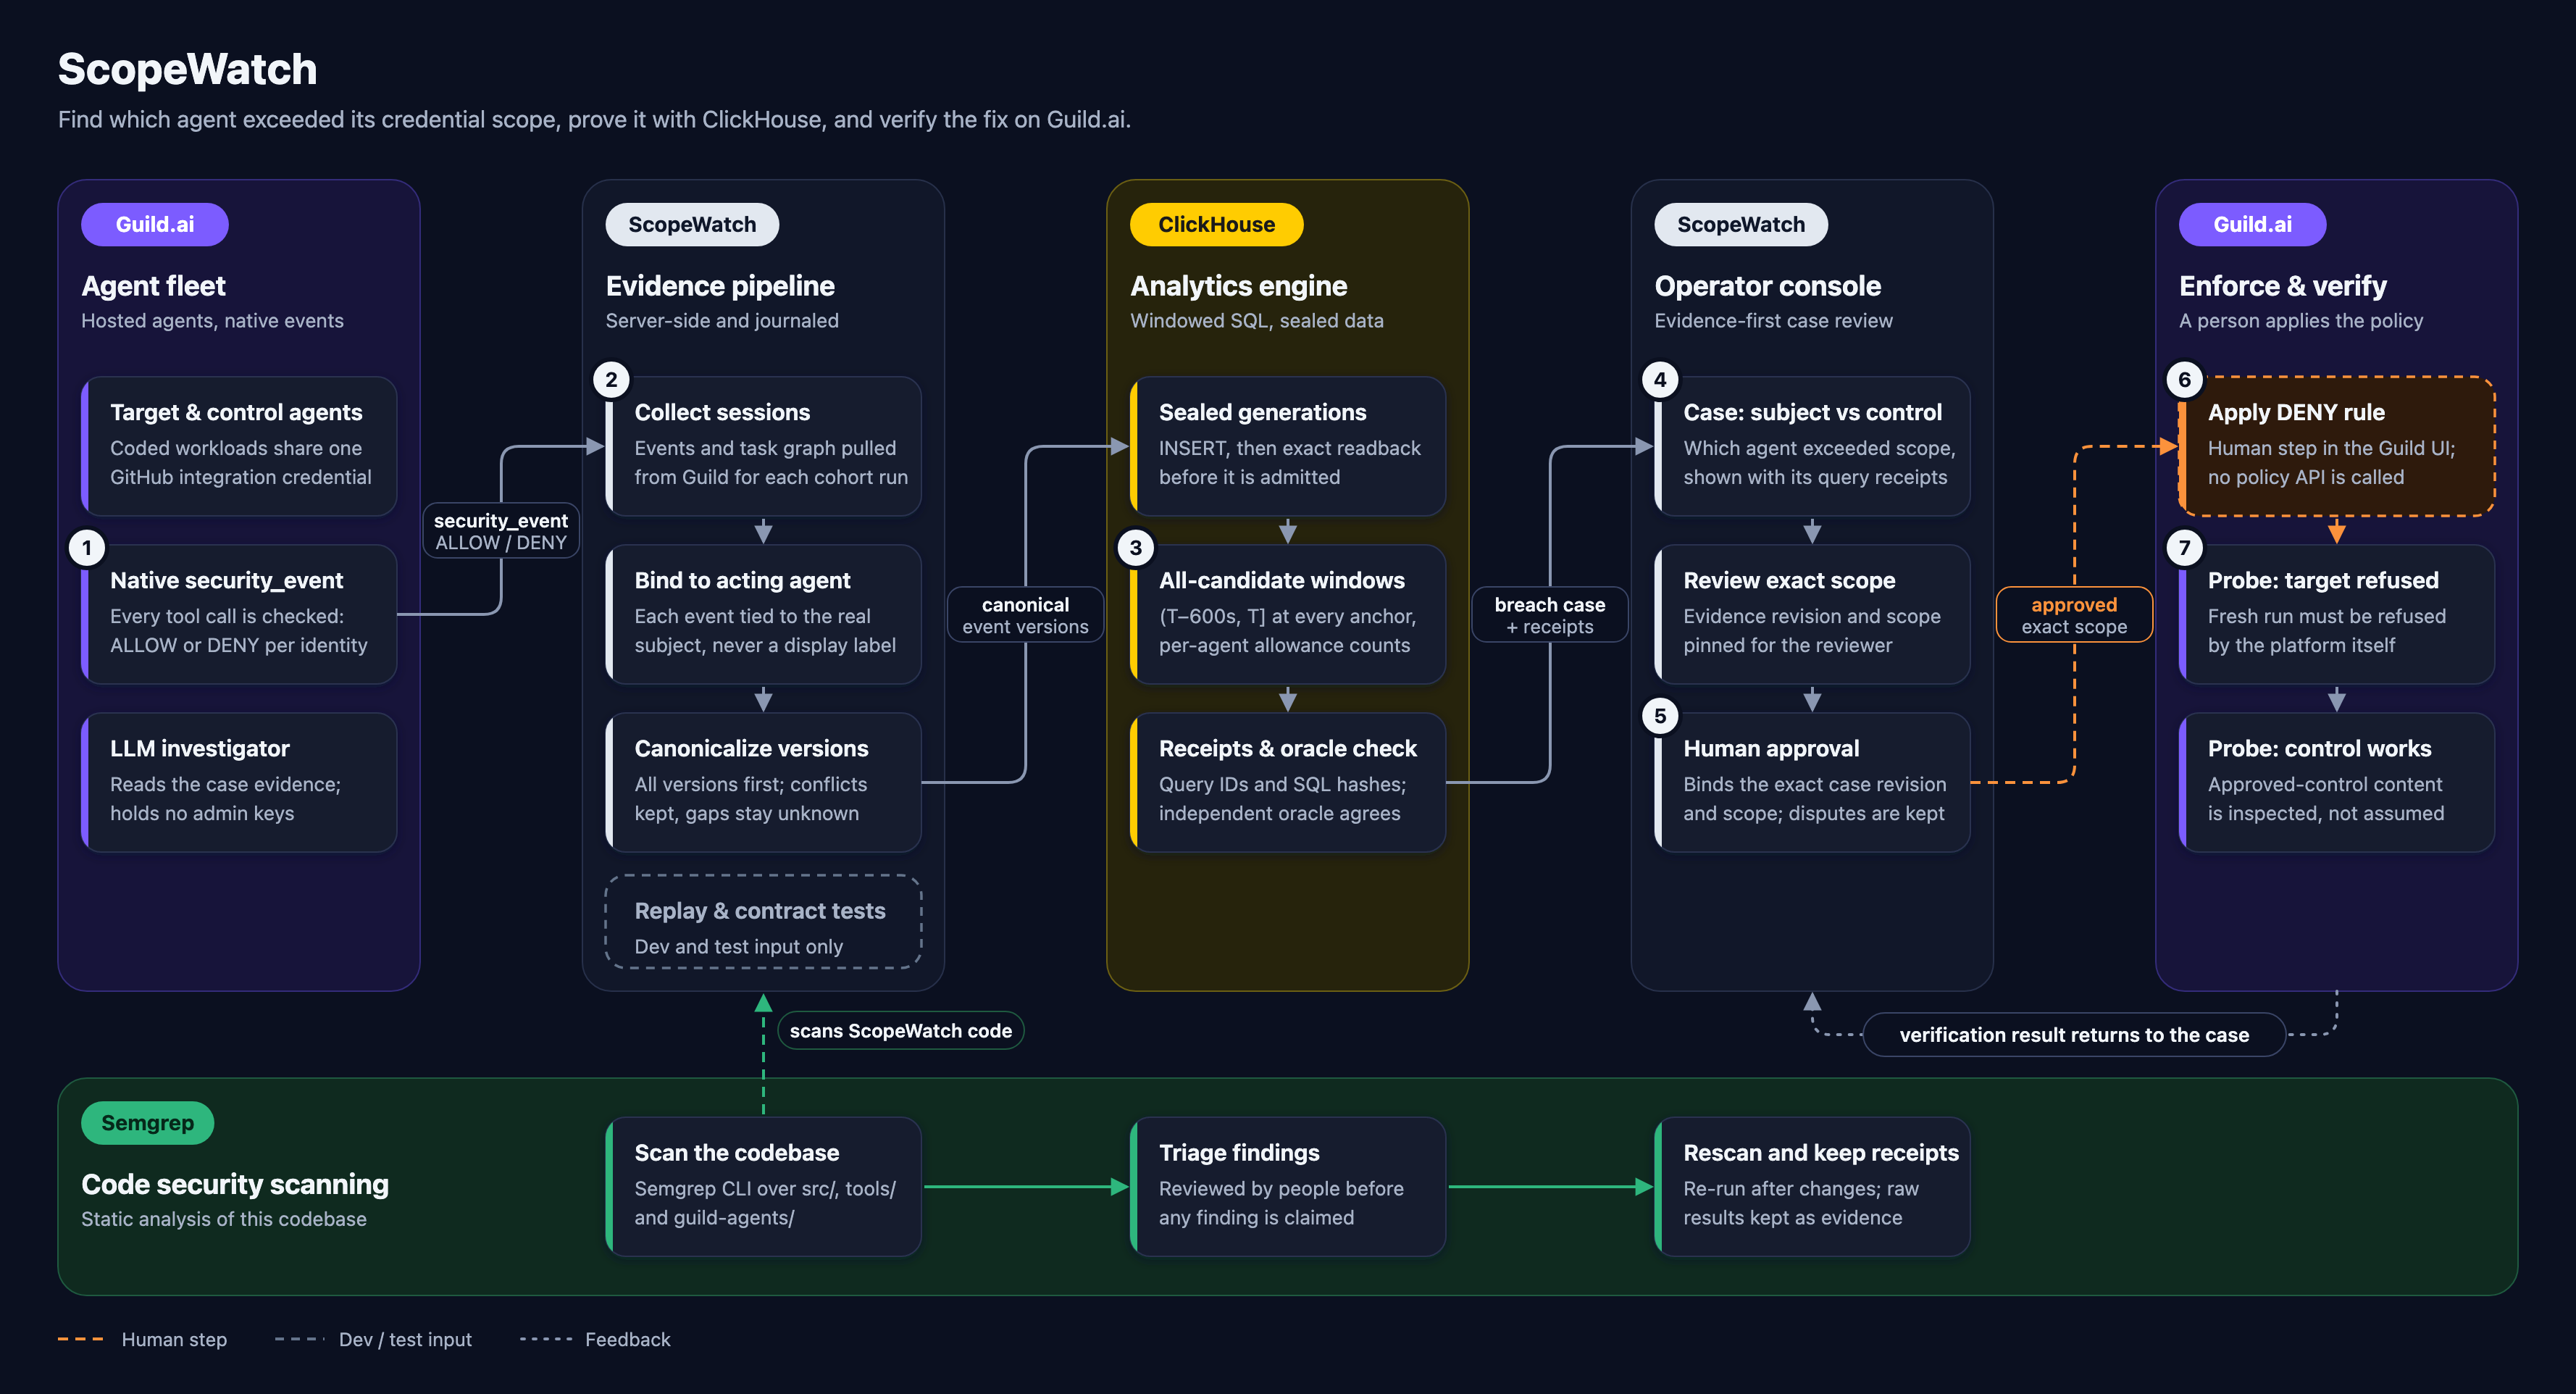
What we built: Least-privilege control for AI agent fleets. When several agents share one credential and one starts overusing a permission (say, after reading a manipulated ticket), ScopeWatch finds that exact agent, blocks only that capability, and proves the approved agents keep working.How it works: We collect every native permission decision and tie it to the agent that actually made it. Then we check each agent against its own allowance in a 10-minute sliding window at every past moment, not just now. An operator reviews the case, approves one exact scope and applies a DENY. Fresh probes must show the target refused and a busier approved agent still getting its expected result. Nothing auto-releases.
Guild.ai: Hosts the fleet: two coded agents built with the agents SDK plus a read-only LLM investigator, launched through an API trigger. Every GitHub tool call emits a native ALLOW/DENY security_event, and we walk the task graph to attribute it. Containment is a DENY rule in Guild's credential policy.
ClickHouse: The decision is made in SQL. Parameterized queries evaluate every agent at every event anchor over (T−600s, T], with conflict-first dedup, exact readback before a case opens, and a receipt per query (query_id, SHA-256, latency). An independent oracle must agree. Runs locally and on ClickHouse Cloud.
Semgrep: We scanned our own AI-assisted codebase with 165 rules (OWASP, secrets, SQLi, AI best practices): 0 findings.
 Guild.ai
 ClickHouse
 Semgrep