tokens&
BrowseFor enterprises
tokens&

Find tools, check provider offers, save a build plan, and share your work when you’re ready.

For buildersFor enterprises

For builders

  • Product launches
  • Builder projects
  • Startup credits and perks
  • Agent Skills
  • Published agents
  • API and agent docs
  • Publish a project

For enterprises

  • Start free company workspace
  • Submit a tool, product, or perk

Community

  • Community
  • Newsletter
  • Events
Xin

© 2026 tokensand, LLC. All rights reserved.

  • Terms
  • Privacy
  • Security
  • Data Processing
  • Status
  1. Hackathon
  2. Project gallery
  3. SentinelEKS
이주안about 1 month agoContributorJudging locked: Event build

SentinelEKS

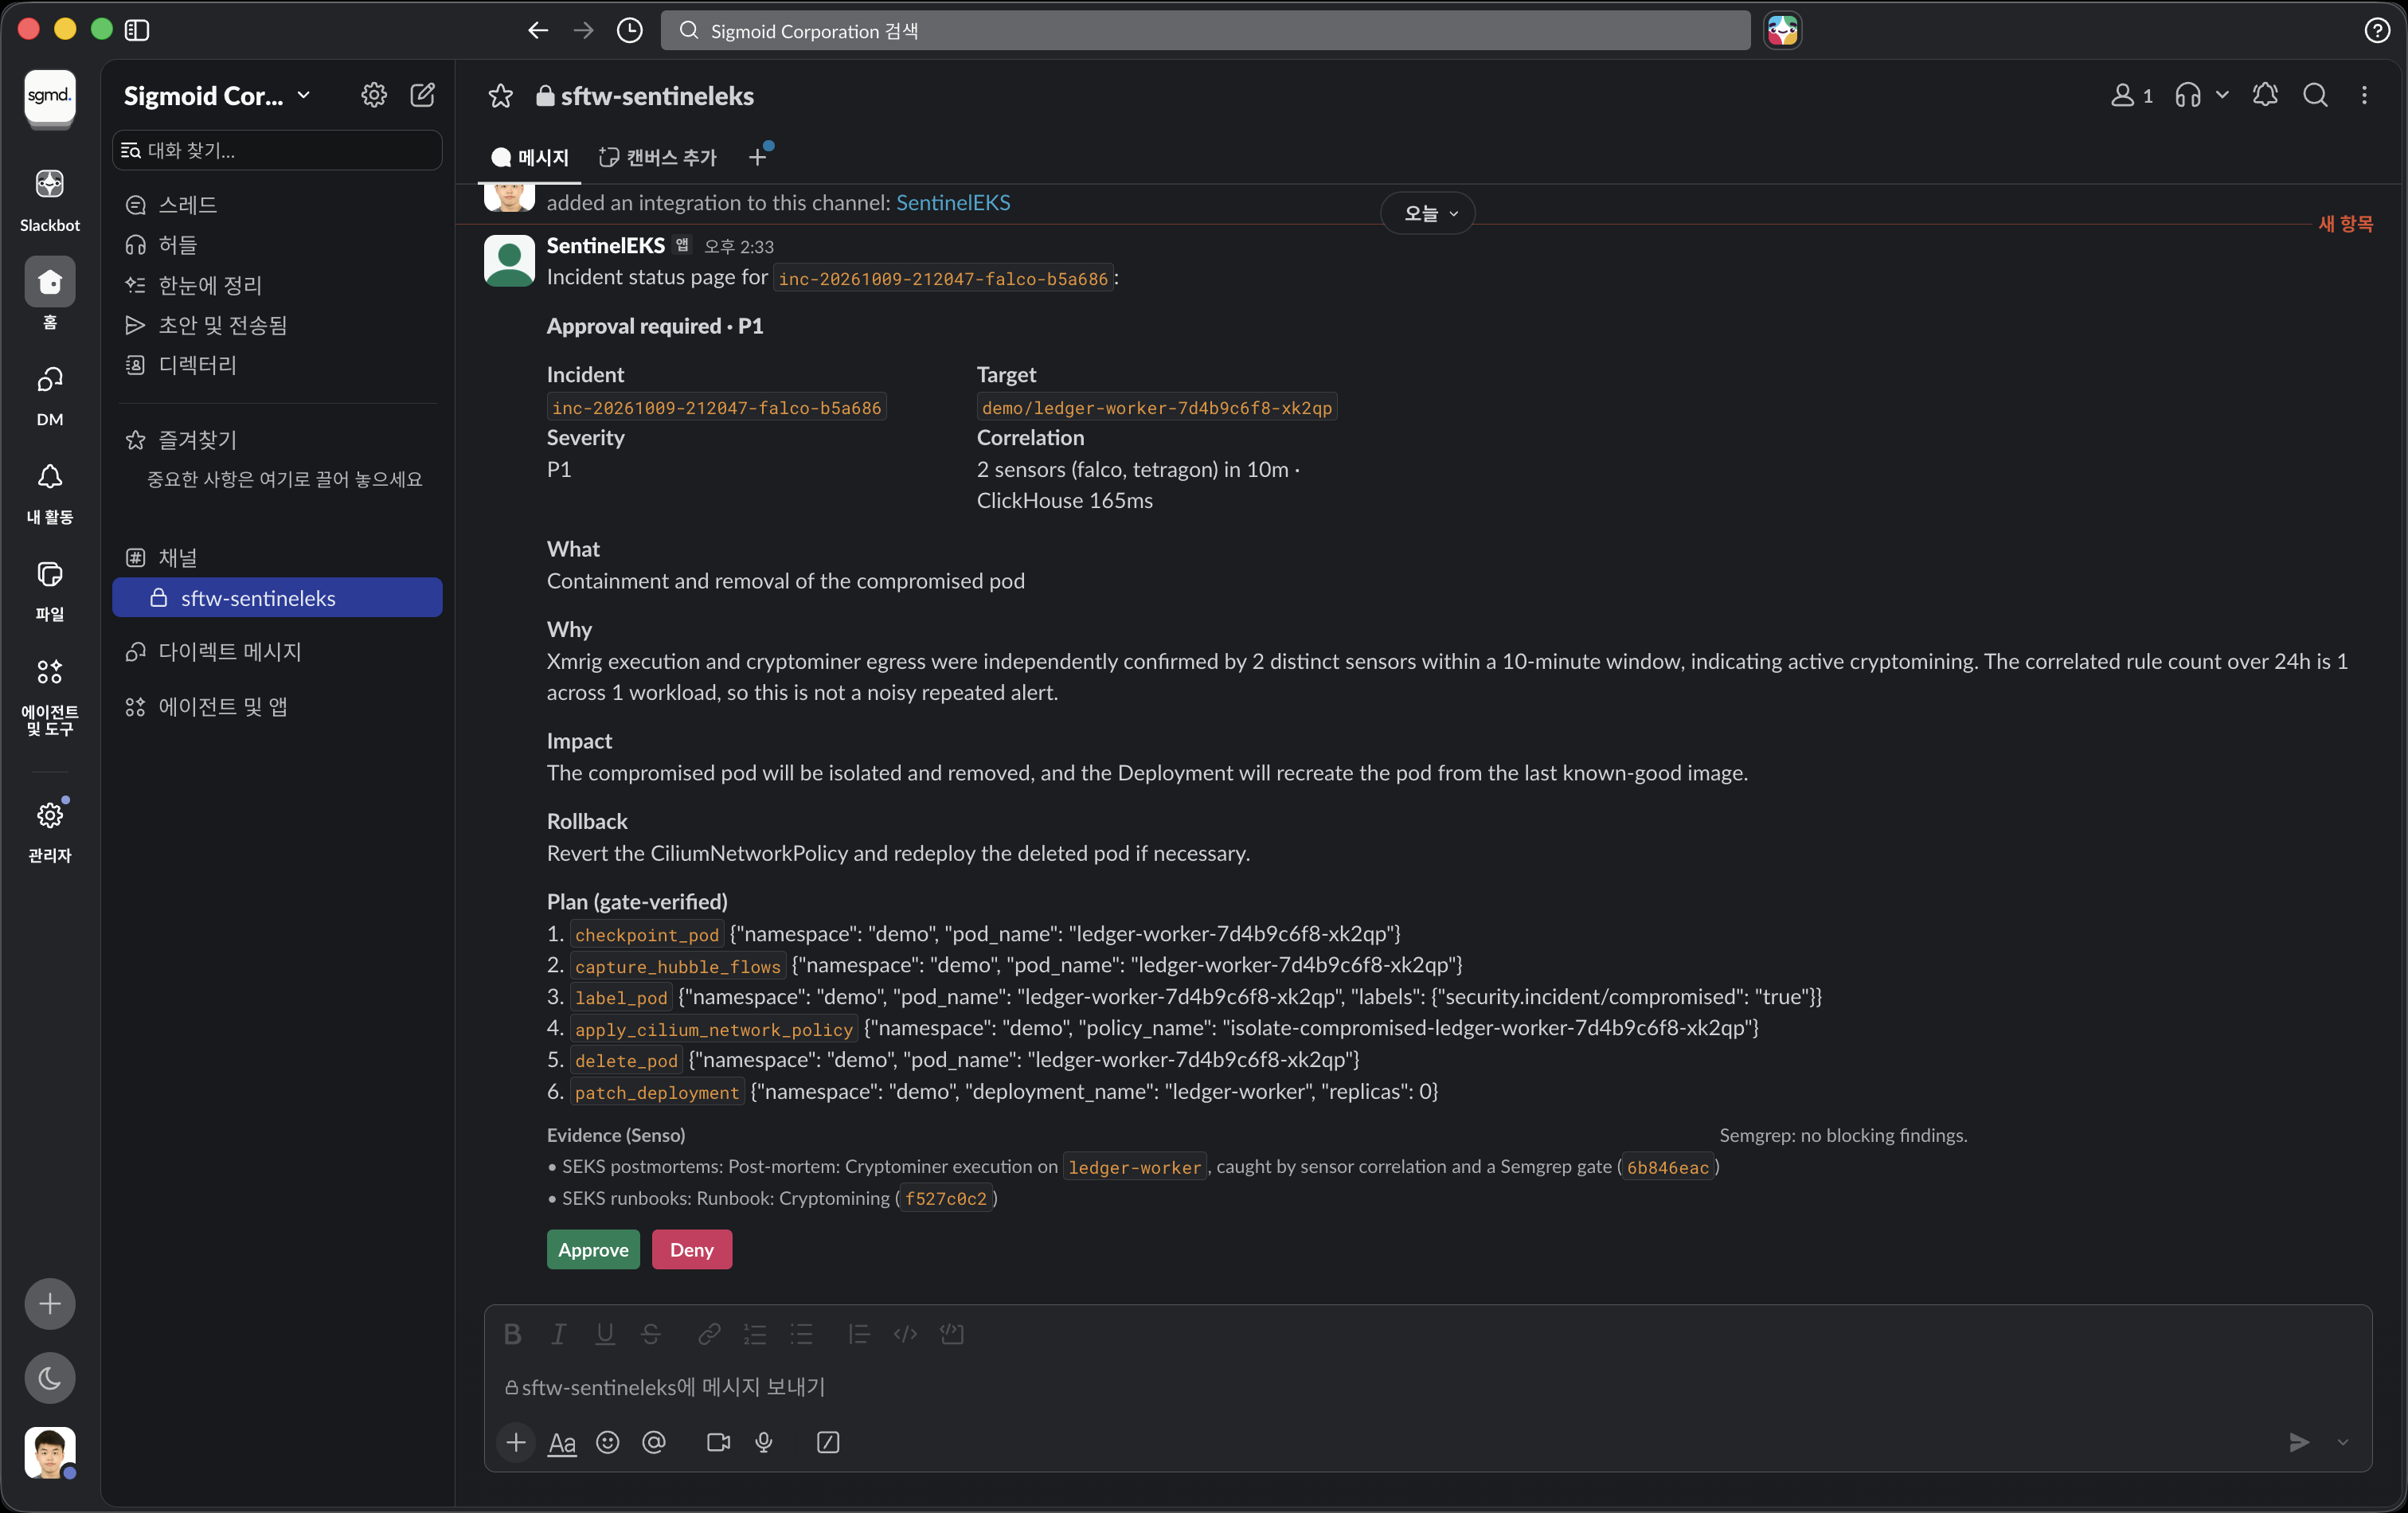
SentinelEKS detects runtime threats on AWS EKS, uses AI grounded in cited runbooks to plan the response, safety-checks it with Semgrep and Pi, and executes only after human approval in Slack.

Community votes recognize the build and do not affect official judging.

Review the project

Start with the source code, then open the demo or video if available.

View GitHub repository
Watch demo videoProject gallery
Demo video
Watch demo video
Project description
SentinelEKS: an autonomous, evidence-grounded security agent for Kubernetes Cryptominers and container escapes move in minutes, while SOC teams juggle separate sensors and AI that suggests actions it can't justify. SentinelEKS closes that loop on AWS EKS: it detects an attack, decides the response using only verified sources, checks its own fix, and contains the threat. A human approves only the destructive step. How the tools work together: 1. Detect and correlate. Falco, Tetragon and GuardDuty events flow through SQS into ClickHouse. Before triage we ask what other sensors saw on the same workload in the last 10 minutes; two or more independent sensors escalate severity, decided by code, not the LLM. 2. Decide with citations. Step Functions runs the agent chain. Bedrock (Claude Haiku) summarizes and triages; Akash-hosted Llama 70B plans the response; Senso returns the official runbook procedure with citations. No citation, no action: the incident goes to a human. 3. Verify before acting. Bedrock (Claude Sonnet) turns the plan into tool calls limited to a whitelist (snapshot, isolate, deny-all NetworkPolicy, SIGKILL, scale-to-0). Semgrep scans the generated manifest and Pi's Code Gatekeeper reviews it. 4. Act and record. Slack shows what, why, impact and rollback; one click executes via EKS MCP. MongoDB stores incident state and an insert-only approval audit; a Slack Canvas status page stays current. Every action is cited, gated and auditable.
Project links
  • GitHub repository
  • Demo video
Tools used
  • MongoDB Atlas logoMongoDB Atlas

    Provider website

    Sign in to visit
Builder

이주안

Builder on tokens&

  • ClickHouse logoClickHouse

    Event resource · ClickHouse docs

    Sign in to visit
  • Akash logoAkash

    Event resource · Akash docs

    Sign in to visit
  • Semgrep logoSemgrep

    Event resource · Claude Code installation instructions

    Sign in to visit
  • SSenso.ai

    Event resource · Docs

    Sign in to visit
  • AAWS
    No link provided