ThreatWatch is a continuous repository defense platform for developers. A user submits a public GitHub repository and chooses a threat lookback window. ThreatWatch reads the dependency manifests and lockfile, checks OSV and GitHub advisories, enriches matches with CISA KEV and EPSS exploit signals, and runs Semgrep to identify relevant code locations without sending source code to the AI.
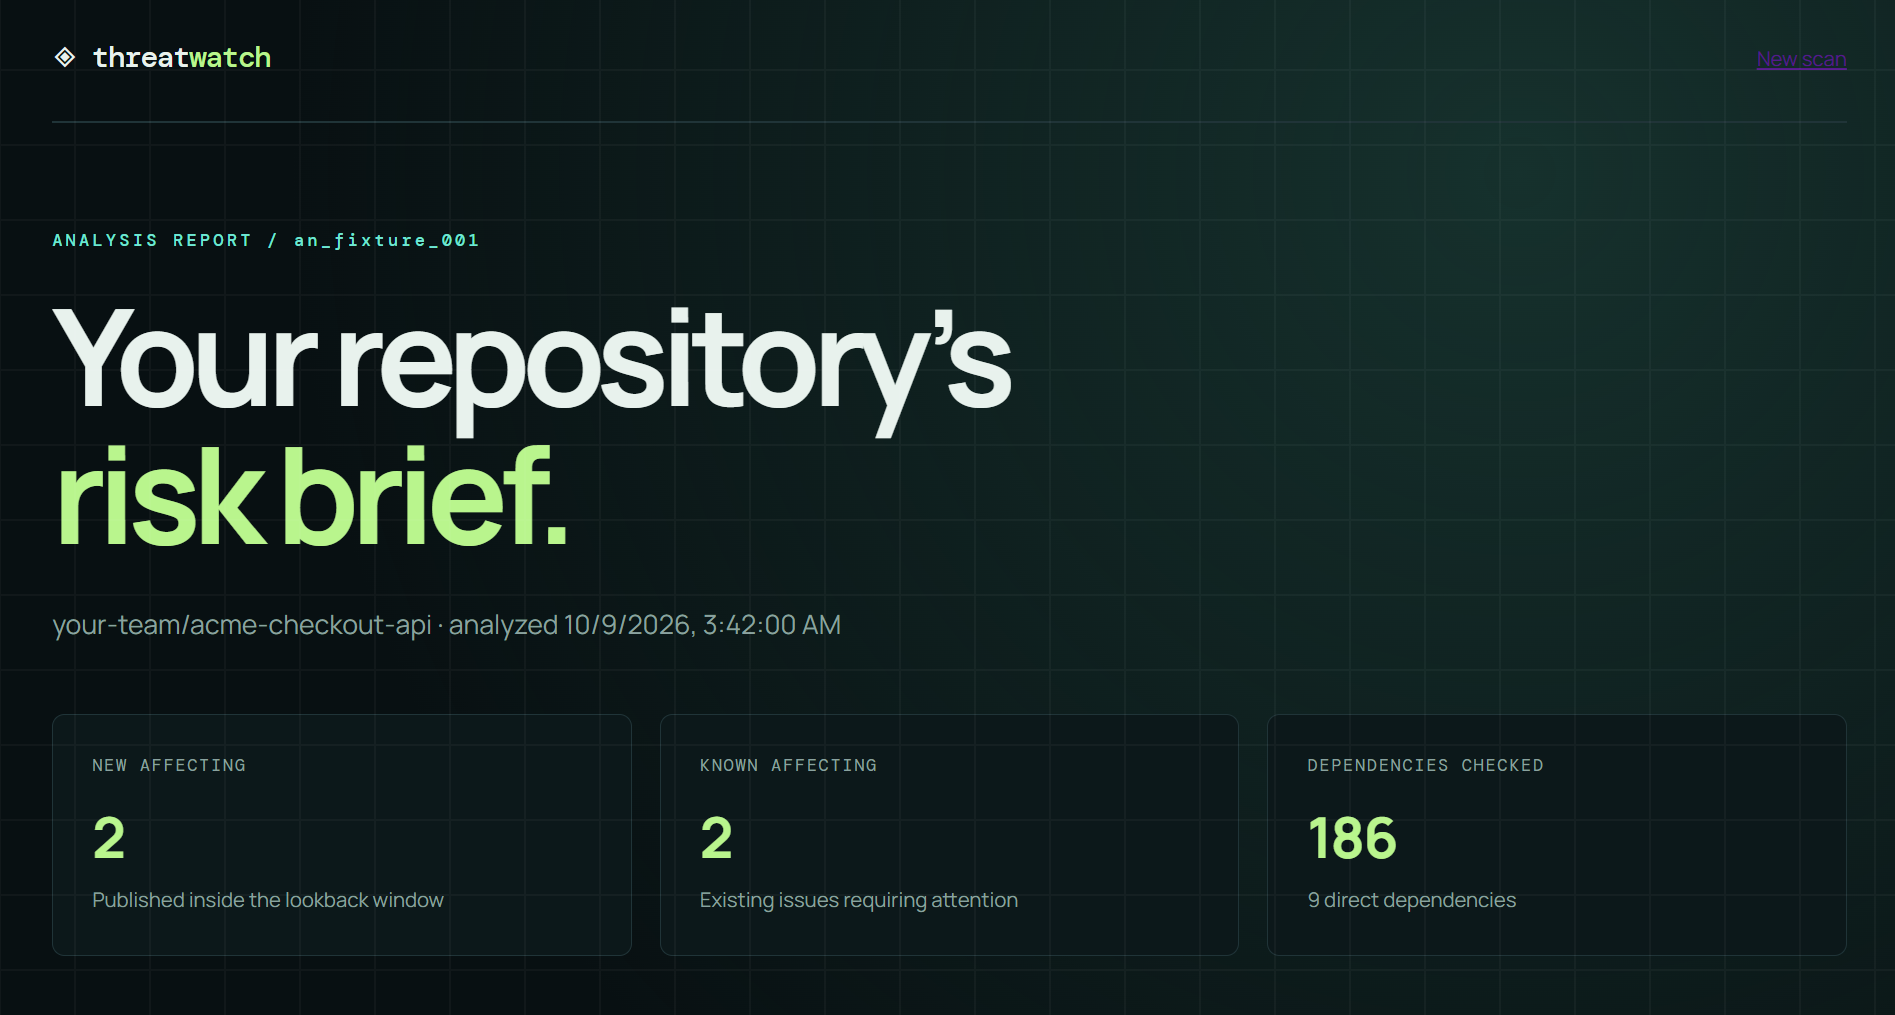
Findings are prioritized using severity, exploitability, recency, dependency usage, and whether a fix is available. AkashML generates a structured explanation of the attack path and remediation. A verification layer rejects unsupported versions, file paths, line numbers, exploit instructions, or claims that the application was breached. The frontend presents the live pipeline and a clear risk report with evidence and verified fixes.
The stack uses Next.js and React for the dashboard, Fastify and TypeScript for the backend, Semgrep for code evidence, public threat intelligence feeds for vulnerability matching, AkashML for safe explanations, and ClickHouse for report persistence.

 ClickHouse